Write-up of a 360 Crowdsourced Testing Simulated Penetration Testing Lab Assessment
The assessment consisted of objective questions and hands-on tasks covering source code analysis, PHP weak typing bypasses, webshell detection and decoding, IP spoofing, Struts2 exploitation, PostgreSQL, SQL injection, and Wireshark packet analysis.
Read in Chinese→0x00 The Assessment Was Mainly Divided into Two Parts
-
The first part consisted of objective questions: single-choice, multiple-choice, and true-or-false questions.
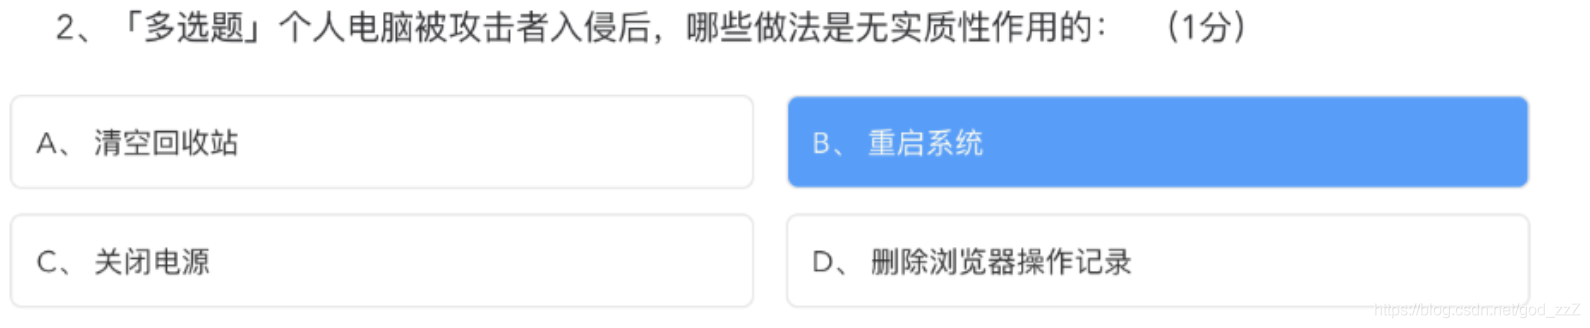
I recorded an interesting question for which I was also unsure of the correct answer.
-
The second part consisted of hands-on tasks:
0x01 Objective Questions
I recorded an interesting question for which I was also unsure of the correct answer. Does anyone know?
0x02: Hands-on Tasks
- A source code analysis question that provided source code and asked for a piece of data
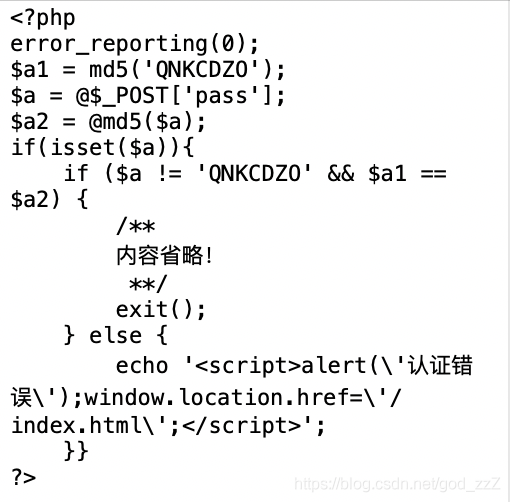
A PHP == weak typing bypass. Since I had never done CTFs before, this one left a strong impression on me.
- A compromised website where you could download the entire site and look for a backdoor
I downloaded the source code and found the backdoor webshell. At a glance, it was an obfuscated one-liner, so I connected to it.
- An encrypted one-line webshell
Just an ordinary one-liner with various decoding steps.
- IP spoofing login via X-Forwarded-For
Login was restricted to the client side.
- A danmaku website
After entering the site, I discovered that it used Struts2, so I ran an automated tool against it.
- The database system of an xxx system: PostgreSQL
I identified it as PostgreSQL, but after connecting, I could not find anything, so I failed to solve it…
- A login form
After clicking around, I discovered an injection vulnerability and ran sqlmap directly.
- Wireshark packet analysis
Someone had changed the database password; the task was to find the new database password.
- Wireshark packet analysis
Find the IP address that deleted a database record.
- Wireshark packet analysis
Find the uploader’s IP address.
0x03 Summary:
-
I felt that the questions assigned to me were not very difficult, so overall it was manageable.
-
Spend a little time learning Wireshark. There are useful techniques—in fact, simply searching for keywords is often enough.
-
The main thing is identifying the question type. Once you know what is being tested, it becomes much easier. Reproduce common CVEs more often and keep practicing.