Uploading a Webshell via PHP_SESSION_UPLOAD_PROGRESS
Environment setup, exploitation requirements, and a CTF example demonstrating how PHP session upload progress can be combined with file inclusion to upload a webshell.
Read in Chinese→0x01 Environment Setup & Exploitation Requirements
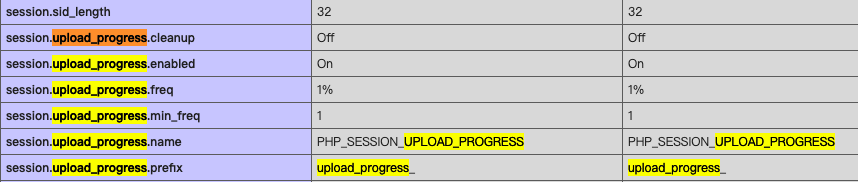
Environment analysis
-
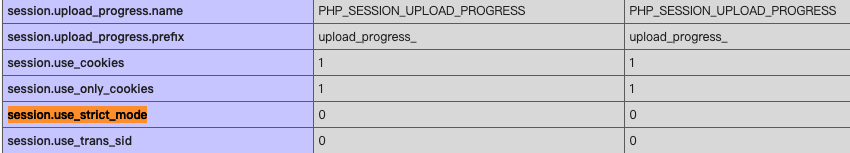
The default value of session.use_strict_mode is 0, which allows users to define their own Session ID.
我们在Cookie里设置PHPSESSID=flag,PHP将会在服务器上创建一个文件:/tmp/sess_flag -
session.upload_progress.prefix consists of the session.upload_progress.name value we construct and is ultimately written to the sess_ file.
Therefore:
- The filename is PHPSESSID=flag, so it is controllable.
- The content can also be written via PHP_SESSION_UPLOAD_PROGRESS.
- If a file inclusion vulnerability exists, it can be used to get a shell.
Under normal circumstances, a race condition is also required:
在默认情况下,session.upload_progress.cleanup是开启的
所以要是处理了所有POST数据,它就会清除进度信息,这个文件就没了

所以需要使用条件竞争:
要在没有处理完post数据的时候就要去触发
0x02 Challenge
This challenge is a web challenge from the Fifth Space CTF.
<?php

if(!isset($_GET['mode'])){
    highlight_file(__file__);
}else if($_GET['mode'] == "eval"){
    $shell = $_GET['shell'] ?? 'phpinfo();';
    if(strlen($shell) > 15 | filter($shell) | checkNums($shell)) exit("hacker");
    eval($shell);
}


if(isset($_GET['file'])){
    if(strlen($_GET['file']) > 15 | filter($_GET['file'])) exit("hacker");
    include $_GET['file'];
}


function filter($var): bool{
    $banned = ["while", "for", "\$_", "include", "env", "require", "?", ":", "^", "+", "-", "%", "*", "`"];

    foreach($banned as $ban){
        if(strstr($var, $ban)) return True;
    }

    return False;
}

function checkNums($var): bool{
    $alphanum = 'abcdefghijklmnopqrstuvwxyz0123456789ABCDEFGHIJKLMNOPQRSTUVWXYZ';
    $cnt = 0;
    for($i = 0; $i < strlen($alphanum); $i++){
        for($j = 0; $j < strlen($var); $j++){
            if($var[$j] == $alphanum[$i]){
                $cnt += 1;
                if($cnt > 8) return True;
            }
        }
    }
    return False;
}

?>
0x03 Exploitation
Upload the HTML file:
name 要对应session.upload_progress.name中的 PHP_SESSION_UPLOAD_PROGRESS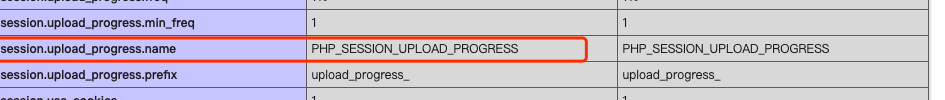
HTML code:
<form action="http://xxxxxxxx.com:8088/" method="POST" enctype="multipart/form-data">
        <input type="text" name="PHP_SESSION_UPLOAD_PROGRESS" value="zzzz" />
        <input type="file" name="file" id="file">
        <input type="submit" name="submit" value="submit">
Then capture the request and insert our one-line webshell into it
[Failed to save the externally linked image. The source site may have hotlink protection enabled. It is recommended that you save the image and upload it directly(img-dwKWo8Vo-1632451391682)(…/Library/Application Support/typora-user-images/image-20210924104028736.png)]
所以文件地址就是 /tmp/sess_zz5
最终利用文件包含获取webshell